Administer
Users, roles & invites
Everything related to team management, access governance, and workspace segmentation lives under Admin — covering users, custom roles, menu access, user groups, workspaces, and invitation lifecycles.
The Users tab (/admin/users) lists every registered workspace member with their role badge, account status (Active, Inactive, Pending), authentication method (SSO provider or local password), and last login timestamp.
Admins can perform full user lifecycle operations:
- Create User: Add local user accounts with assigned roles.
- Edit Member Details: Update names, roles, and company affiliations.
- Deactivate & Reactivate: Temporarily suspend or restore user accounts without deleting history.
- Reset Password: Generate a secure password reset link or trigger an administrative password reset.
- Transfer Ownership: Promote or reassign administrative privileges.
Password rules
Section titled “Password rules”Every password set in DataSquares follows the same rules: when someone signs up, accepts an invitation or resets a forgotten password, when an admin creates an account or sets a password, and when you change your own. A password must:
- be 8 to 128 characters long;
- not be one of the 10,000 most commonly used passwords, or a common first name or surname, even with numbers or symbols added or letters swapped for look-alikes (
Password123!,P@ssw0rdandMichael1!are all refused); - not be a simple pattern such as
aaaaaaaa,12345678orqwertyuiop, with or without numbers added; - not be built on the person’s own email address or name, or on the name DataSquares.
There are no rules about mixing kinds of characters: a long phrase of ordinary words is a good password. The check runs inside DataSquares against a built-in list, and the password is never sent anywhere. A refused password says which rule it broke. Passwords already in use keep working; the rules apply when a password is set.
Walkthrough: manage users
Section titled “Walkthrough: manage users”Create a person, change their access, reset a password and deactivate them. The steps use a sample person, “Guide A - Priya Nair”.
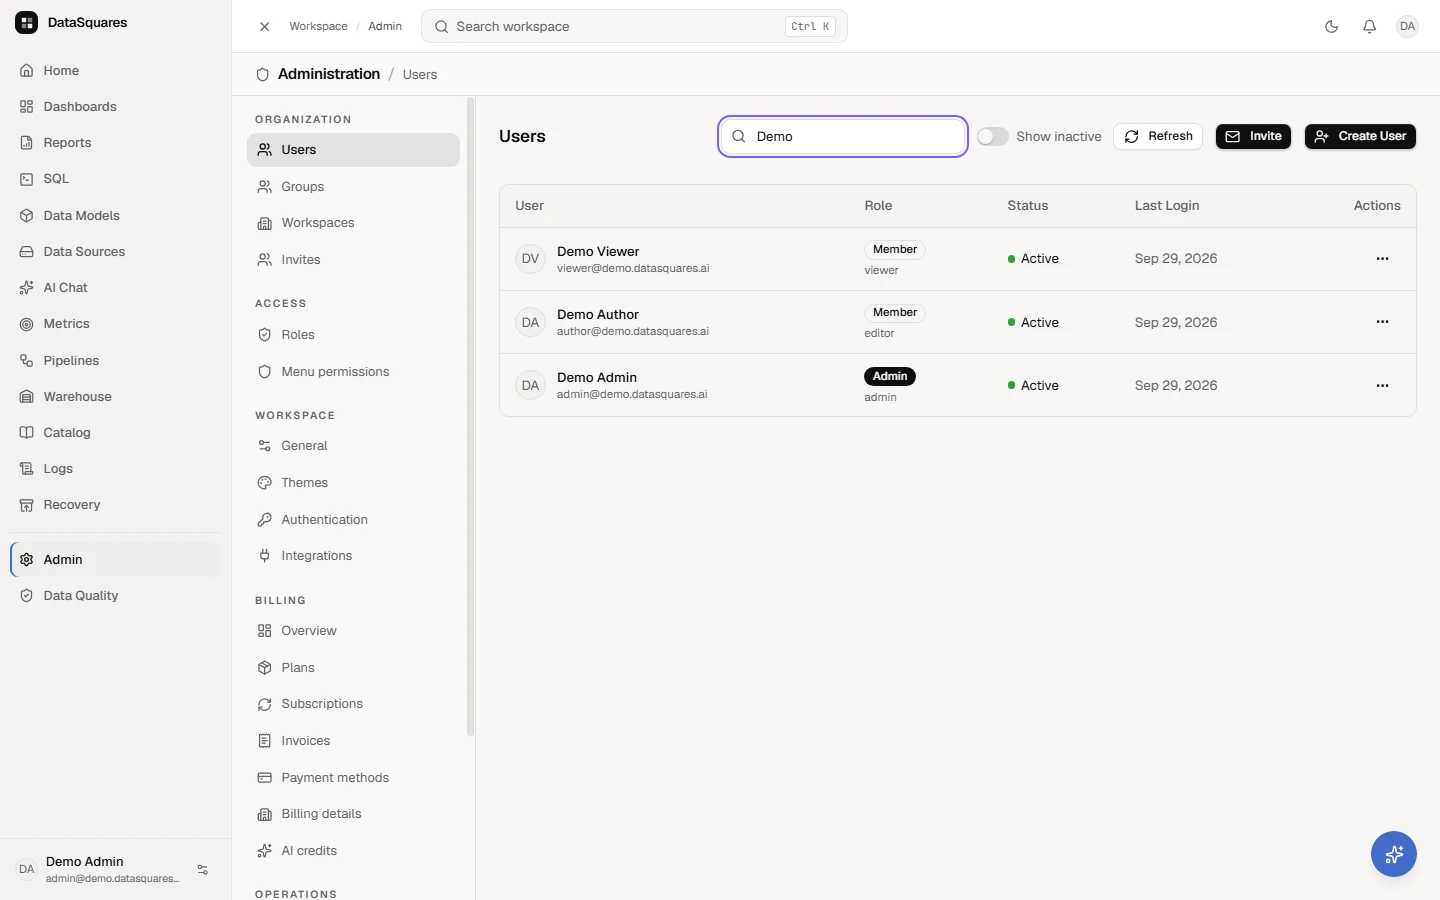
Open Admin, then Users. The table lists everyone in the company with their role and status. Search by name or email to narrow it.
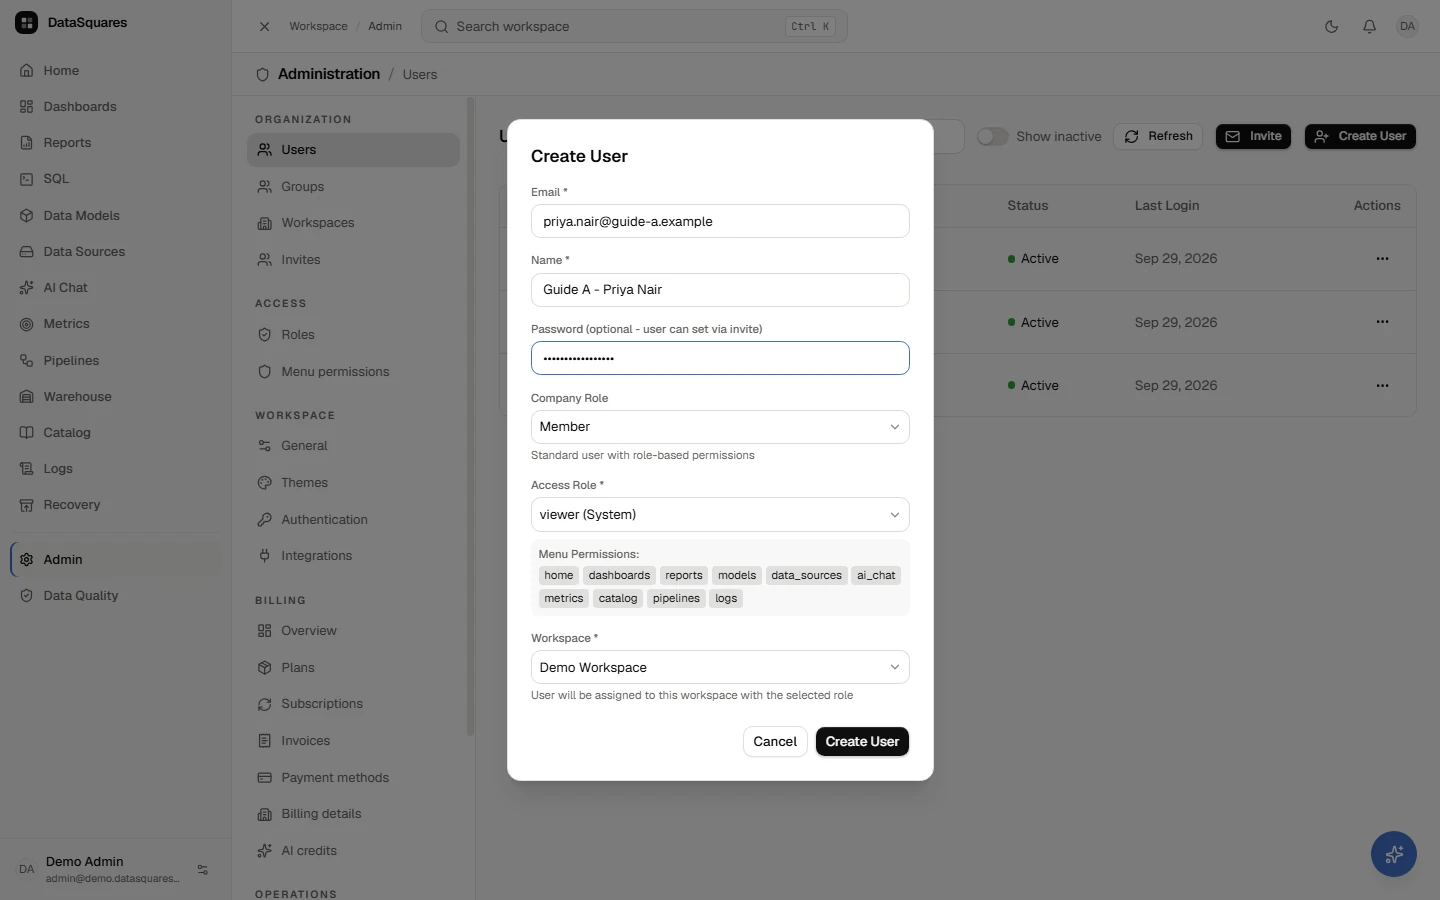
Choose Create User. Enter the email and name, set a temporary password (or leave it blank to invite the person instead), then pick the company role, the access role and the workspace.
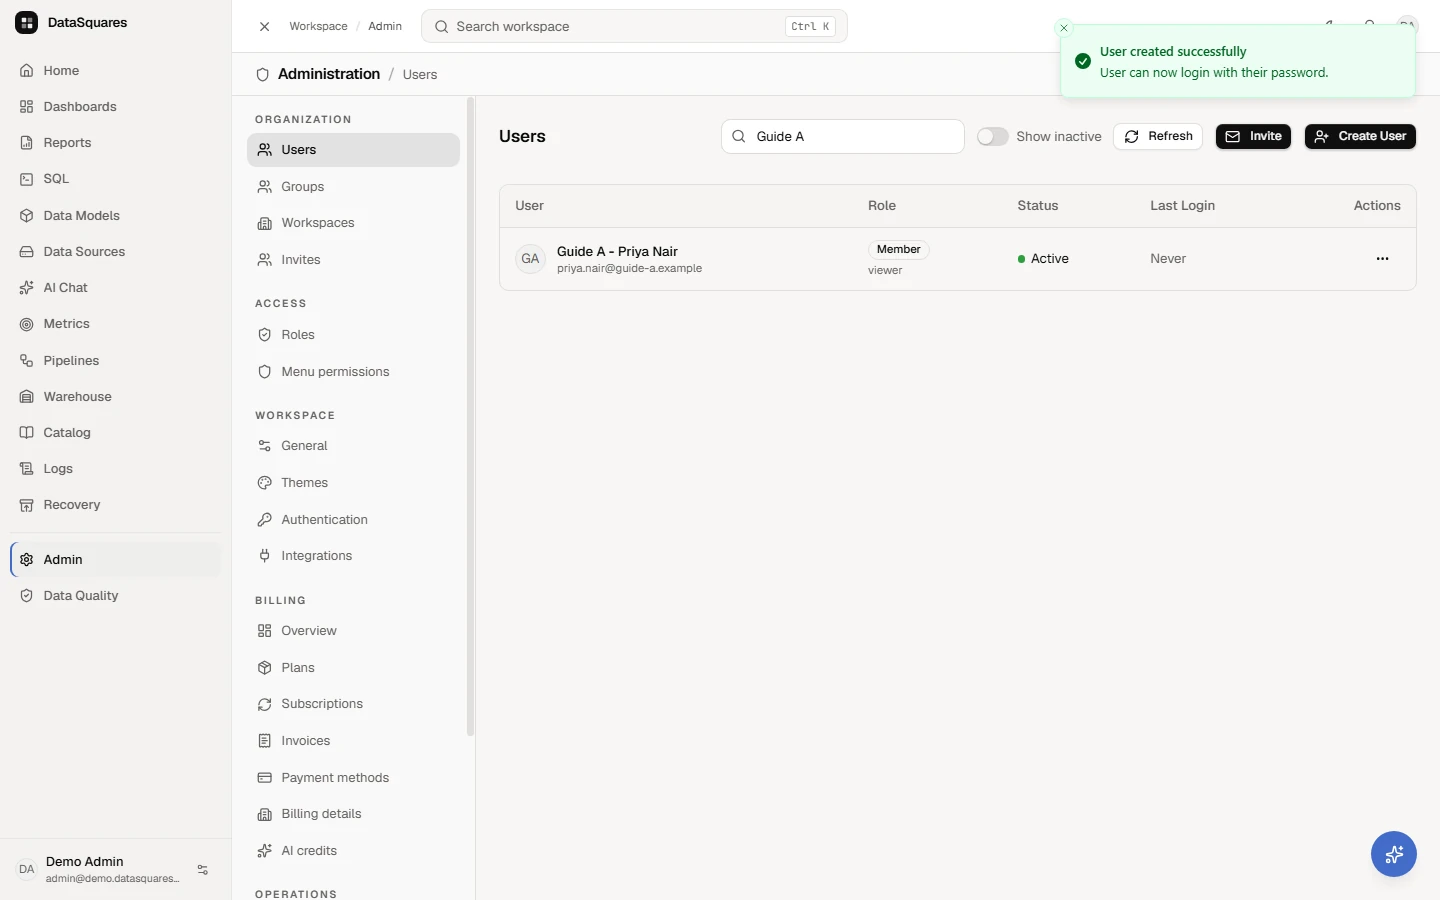
The new person appears in the list, active and ready to sign in.
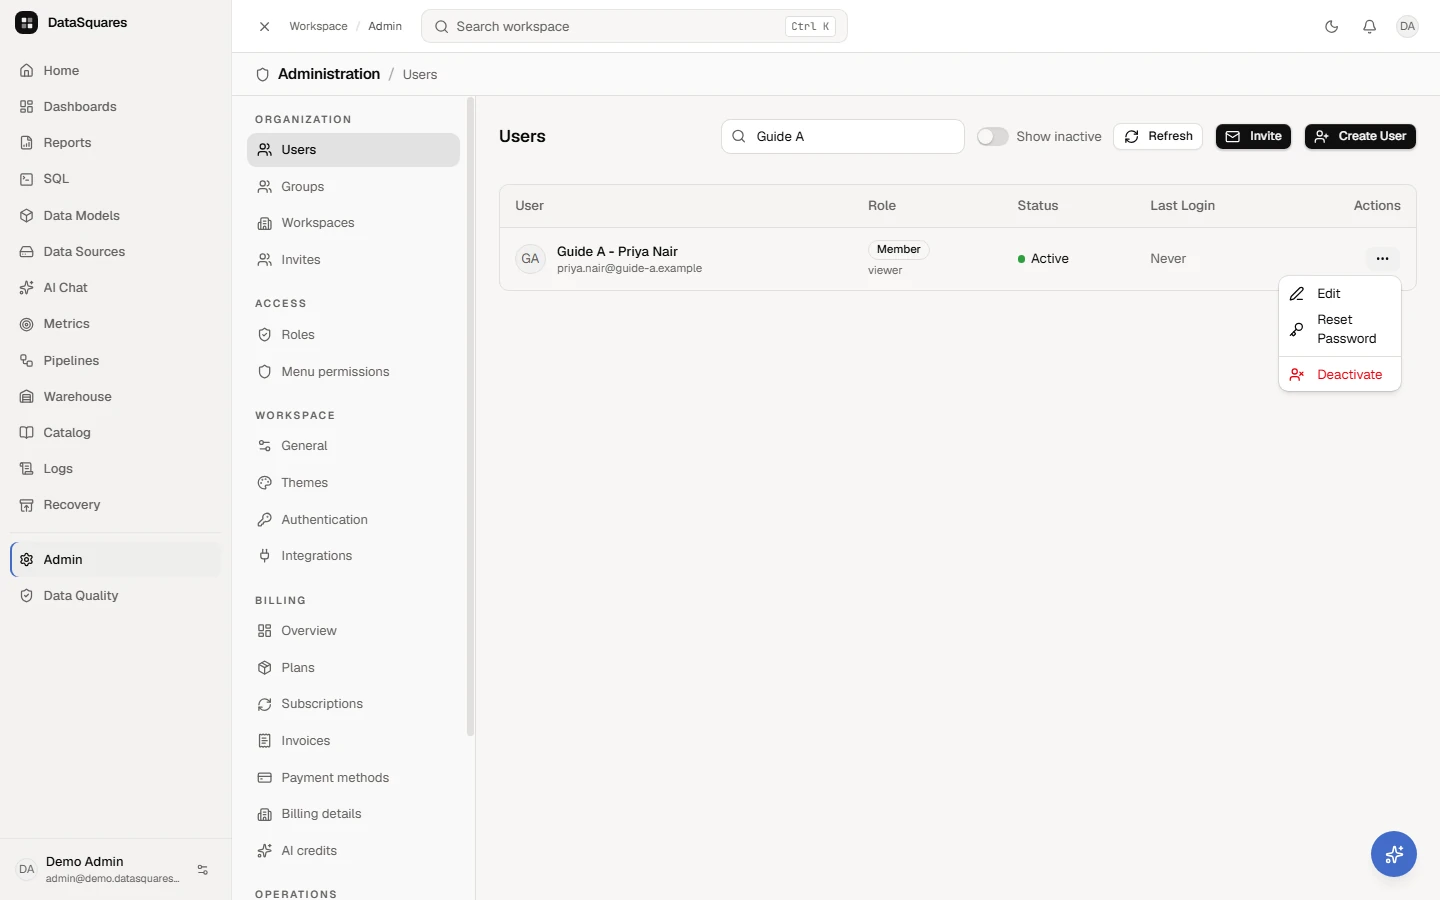
Open the Actions menu on a row. From here you can edit the person, reset their password or deactivate them.
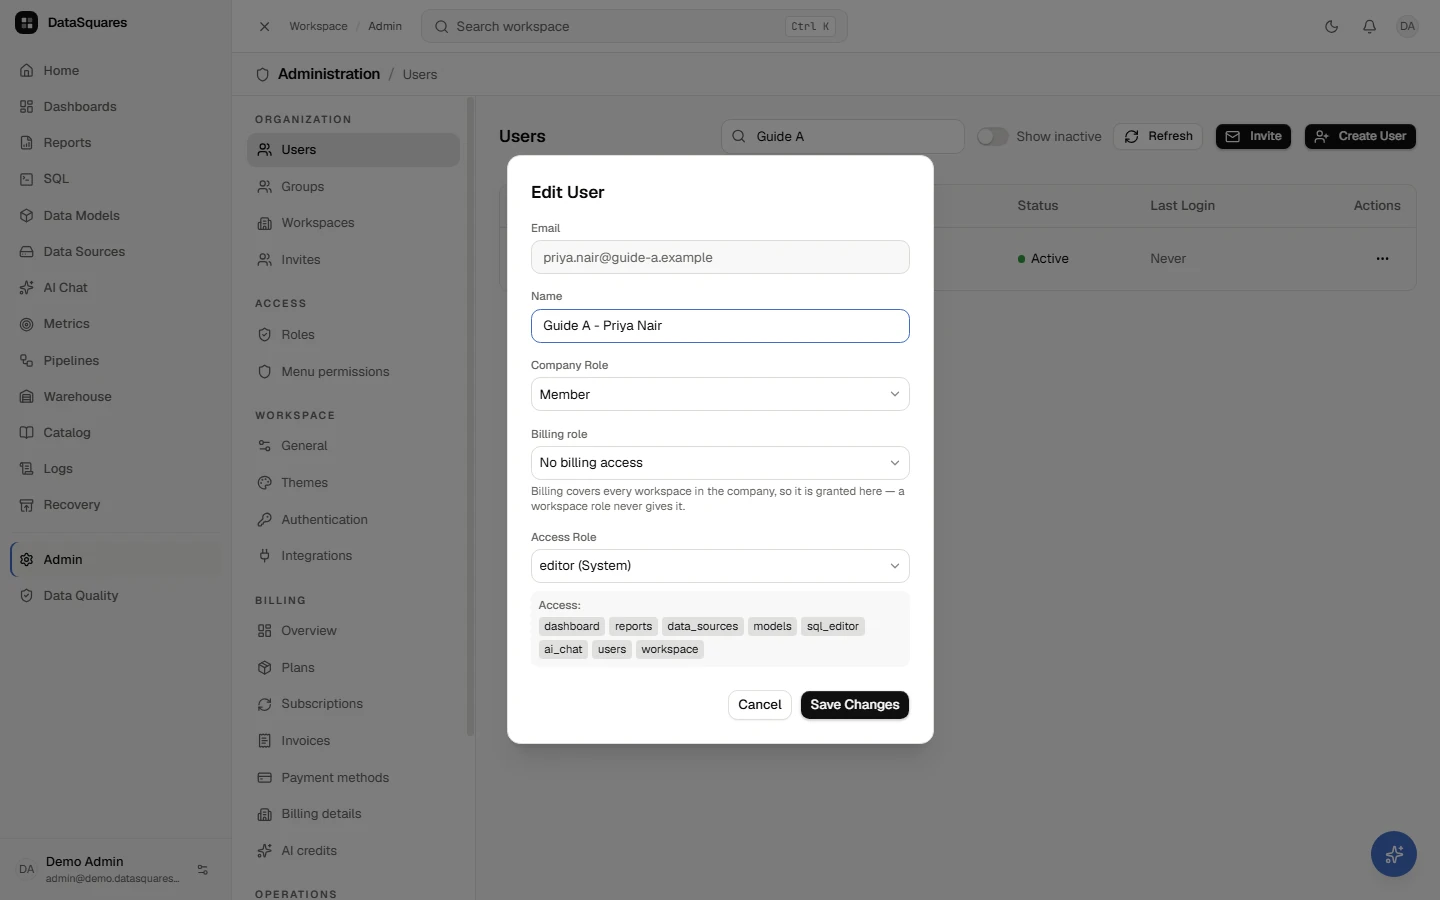
Choose Edit and change what you need: the name, company role, billing role or access role. Here the access role goes from viewer to editor. Then choose Save Changes.
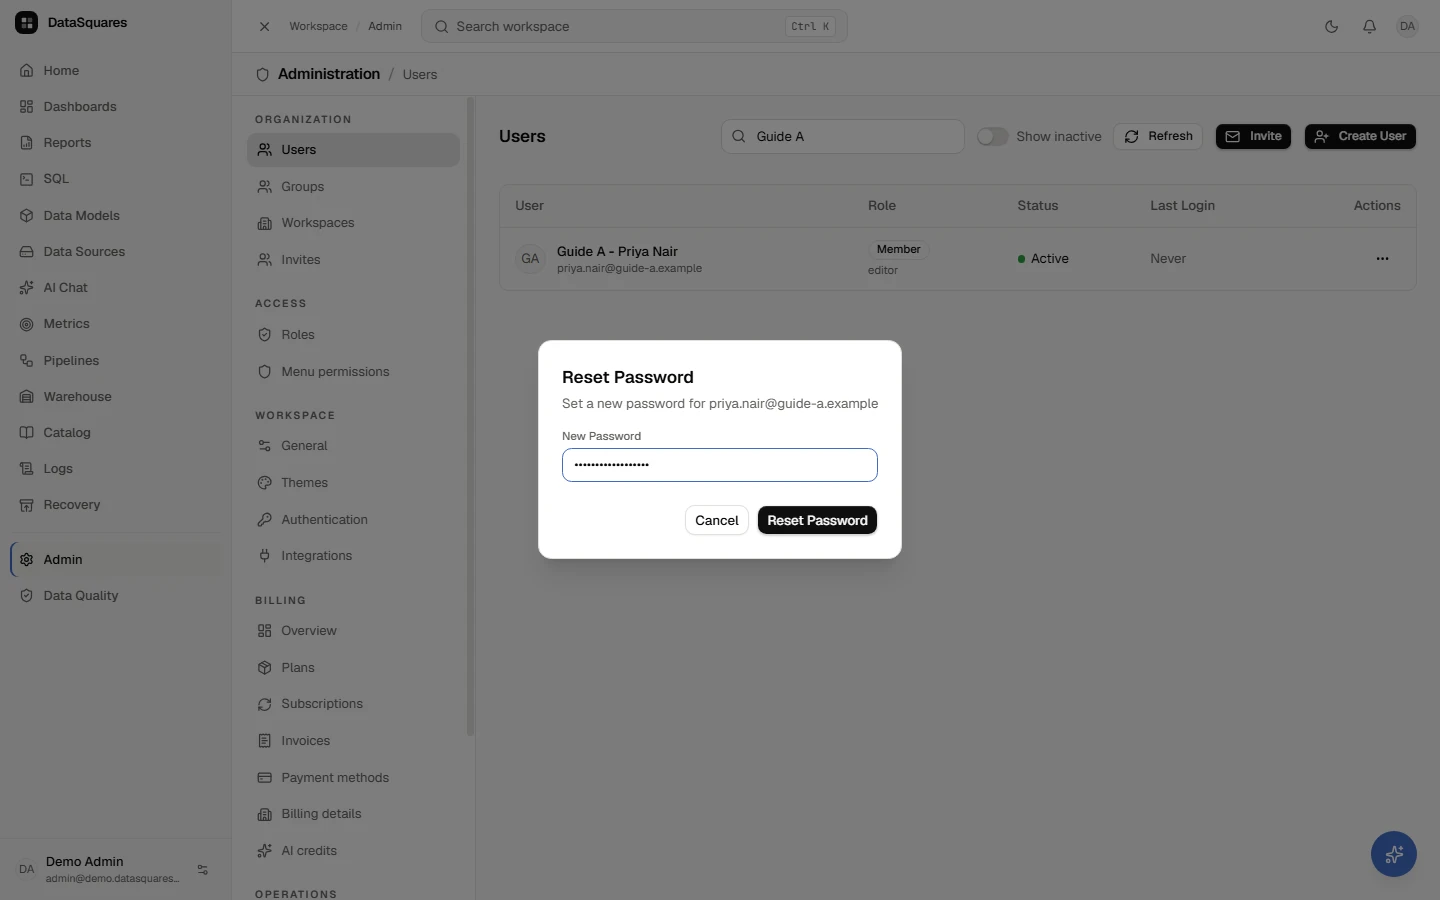
Choose Reset Password on the row, type a new password of at least eight characters, and confirm. Share it with the person securely.
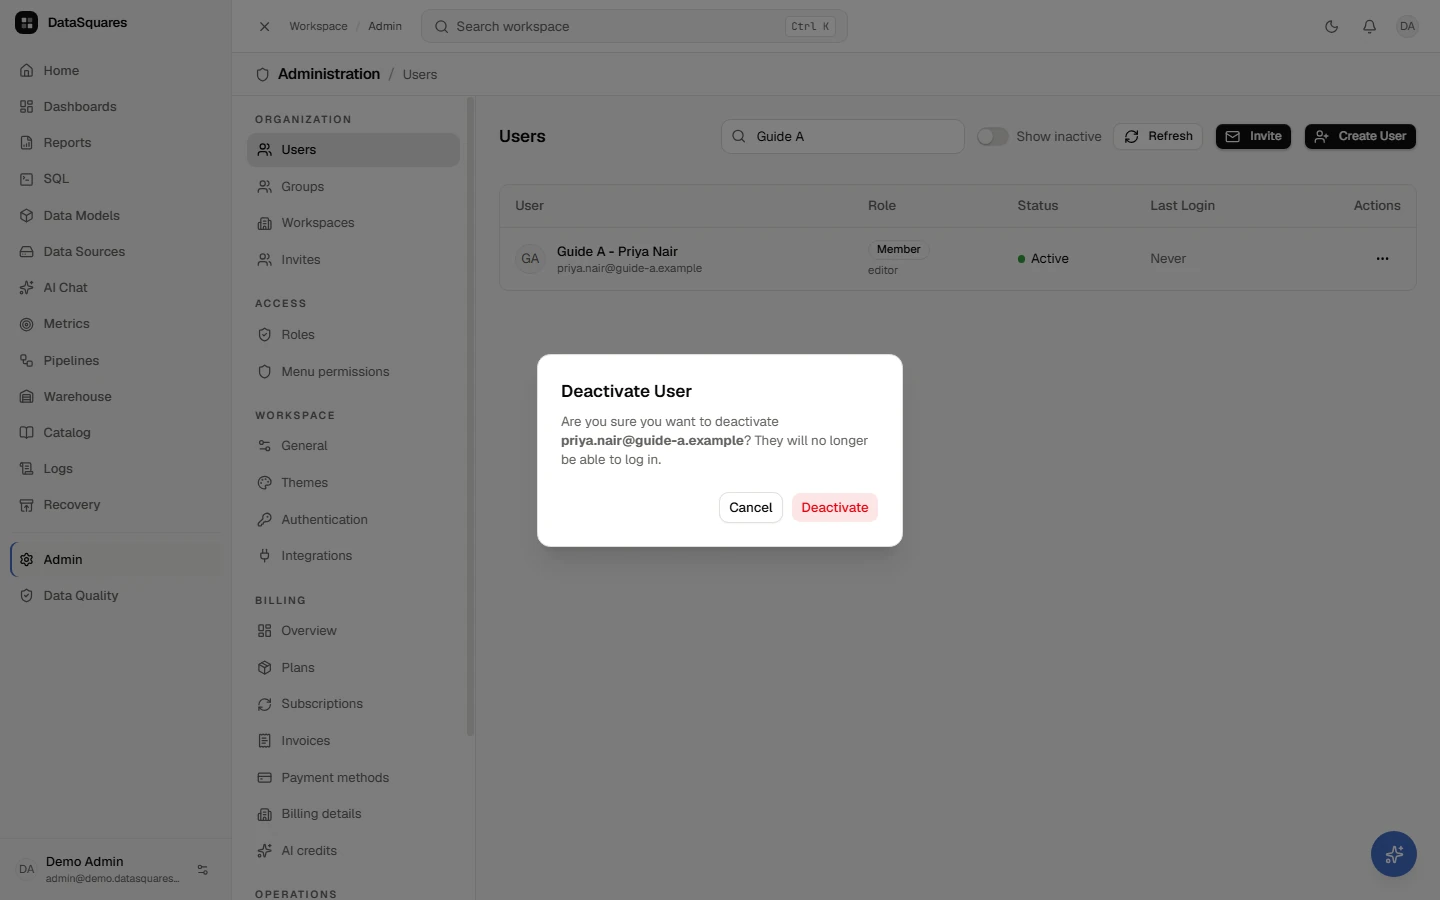
Choose Deactivate to stop someone signing in, for example when they leave. Their content stays.
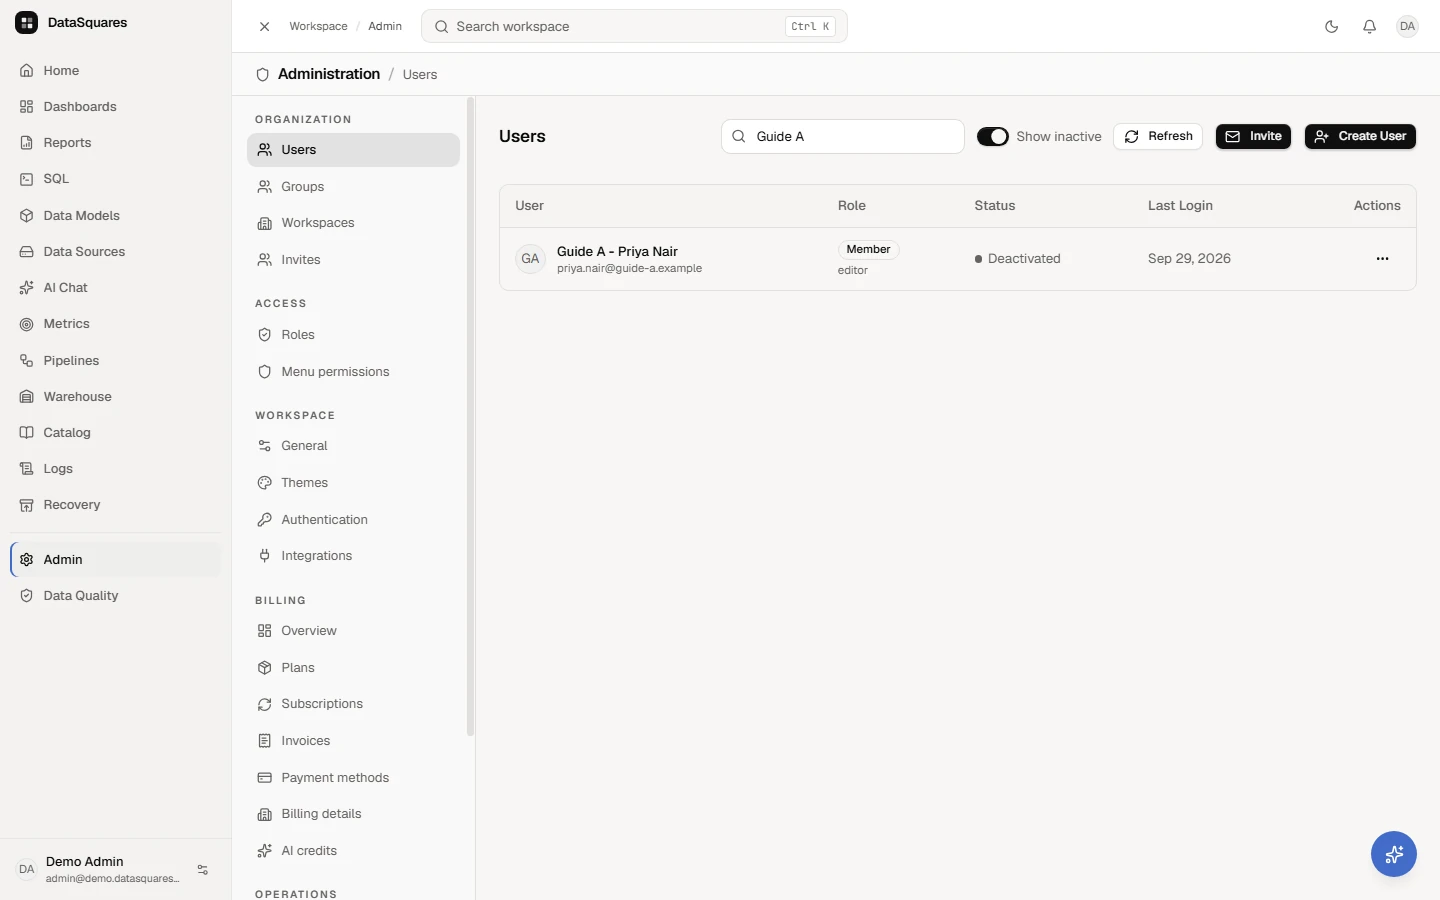
Turn on Show inactive to see deactivated people. They are listed as Deactivated.
Deleting a person’s data
Section titled “Deleting a person’s data”Deactivating a person keeps their account, what they made and their history. To have a person’s data deleted, ask the platform’s operators; the person can also ask themselves. On the hosted service, the privacy notice’s Deleting your data section says how. The operators confirm the request with you before they act.
Your request covers your organization only. The operators can move what the person owns to a member you name, erase their AI data and personal settings in your organization, and remove them from it. Their account, and any other organization they belong to, stay until they ask themselves. What they made at work stays with your organization.
If your organization provisions people through SCIM, unassign the person in your identity provider as well, or its next sync can add them back. When the person asks for their whole account to be deleted, it is anonymised only once no identity provider manages it.
An account anonymised at the person’s request shows as “Deleted user” and can’t be activated again: Reactivate, resending its invitation and accepting an invitation still pending for it are refused, saying so.
People’s attributes
Section titled “People’s attributes”A person’s attributes, such as their region, department or cost center, are values row-level security can read: a policy can keep only the rows whose column holds one of the person’s values. They belong to the company, so they apply in every workspace.
Company admins open them from a person’s row in Users: Actions → Attributes.
- Each attribute has a name and one or more values, one per line. A name is lower-case letters, digits and
underscores, starting with a letter (
region,cost_center). Values are matched exactly; blank lines and repeated values are dropped. - Add an attribute adds one; the cross beside an attribute removes it. Save attributes replaces the person’s admin-set attributes with the list, and policies read the new values from the next query.
- Attributes your identity provider manages through SCIM are listed apart and can’t be changed here: change them in the provider. A name the provider manages, a name given twice and an attribute with no value are refused with the reason.
- A person holds at most 100 attributes, an attribute at most 500 values of up to 500 characters each; more is refused, never cut.
Every change is written to the Audit Log as user.attributes_updated, with the values before
and after: attributes decide which rows a person sees. It belongs to no workspace, so it shows in the
company audit view. The API is GET and PUT /api/users/{id}/attributes,
and GET /api/users/attributes lists the names held in the company with how many hold each.
System roles
Section titled “System roles”Every workspace provisions three immutable system roles:
| Privilege | Admin | Editor | Viewer |
|---|---|---|---|
| View dashboards & reports | ✓ | ✓ | ✓ |
| AI chat & card insights | ✓ | ✓ | ✓ |
| Author & edit dashboards, reports, and models | ✓ | ✓ | — |
| Create and manage data sources & pipelines | ✓ | ✓ | — |
| SQL editor & visual query builder | ✓ | ✓ | — |
| Share dashboards & manage embeds | ✓ | ✓ | — |
| Export data (PDF, PPTX, CSV, Excel, Image) | ✓ | ✓ | — |
| Delete workspace content | ✓ | — | — |
| Manage users, roles, licenses, compute & billing | ✓ | — | — |
All three roles have the AI Chat permission, which every AI feature needs. Which AI features each role may use, and AI as a whole, are set under Administration → AI: by default a Viewer has the chat, Explain and Analyze, the report AI and metric digests’ AI sentences, and the other roles have every AI feature. See Control AI in a workspace.
Custom roles & granular permissions
Section titled “Custom roles & granular permissions”When access requirements fall between system roles, create a Custom Role under the Roles tab (/admin/roles):
- Name & Description: Define identity and role scope.
- Granular Permission Matrix: Configure View / Create / Update / Delete permissions per system area (Dashboards, Reports, Models, Sources, Pipelines, Warehouse, Queries, Alerts, Data Quality, Admin).
- Menu Visibility & Discovery: Control which sidebar items and navigation elements appear for users assigned to the role.
- Role Safety: System roles are protected against modification or deletion, and custom roles cannot be deleted while assigned to active users.
Delegating administration
Section titled “Delegating administration”Each Administration destination has its own permission. A custom role can hold Groups, the Themes and Integrations workspace settings, each of the seven Billing permissions (any one of them shows the one Billing item, and each shows its part of the page and opens its sheet: who sees which part), Usage, Experience, Audit log and AI escalations; it sees the destinations it holds and nothing else, so a role granted only Audit log lands on the audit log with no other entries in the Administration menu. Users, Workspaces, Invites, Roles, Menu permissions, the General, Authentication and AI settings and Compute appear only for company administrators, whatever a role holds. The Admin permission only opens the Administration area. Company administrators see every destination (Deployment license only on a private server).
Changing groups (creating, renaming, deleting, adding or removing members) needs the Groups permission, because groups carry access to shared content. Anyone can still pick a group when sharing.
Walkthrough: create a role
Section titled “Walkthrough: create a role”Build a custom role that can only view dashboards and reports, change it, then delete it.
Open Admin, then Roles. The three system roles (admin, editor, viewer) are built in and locked. Custom roles you create sit beside them.
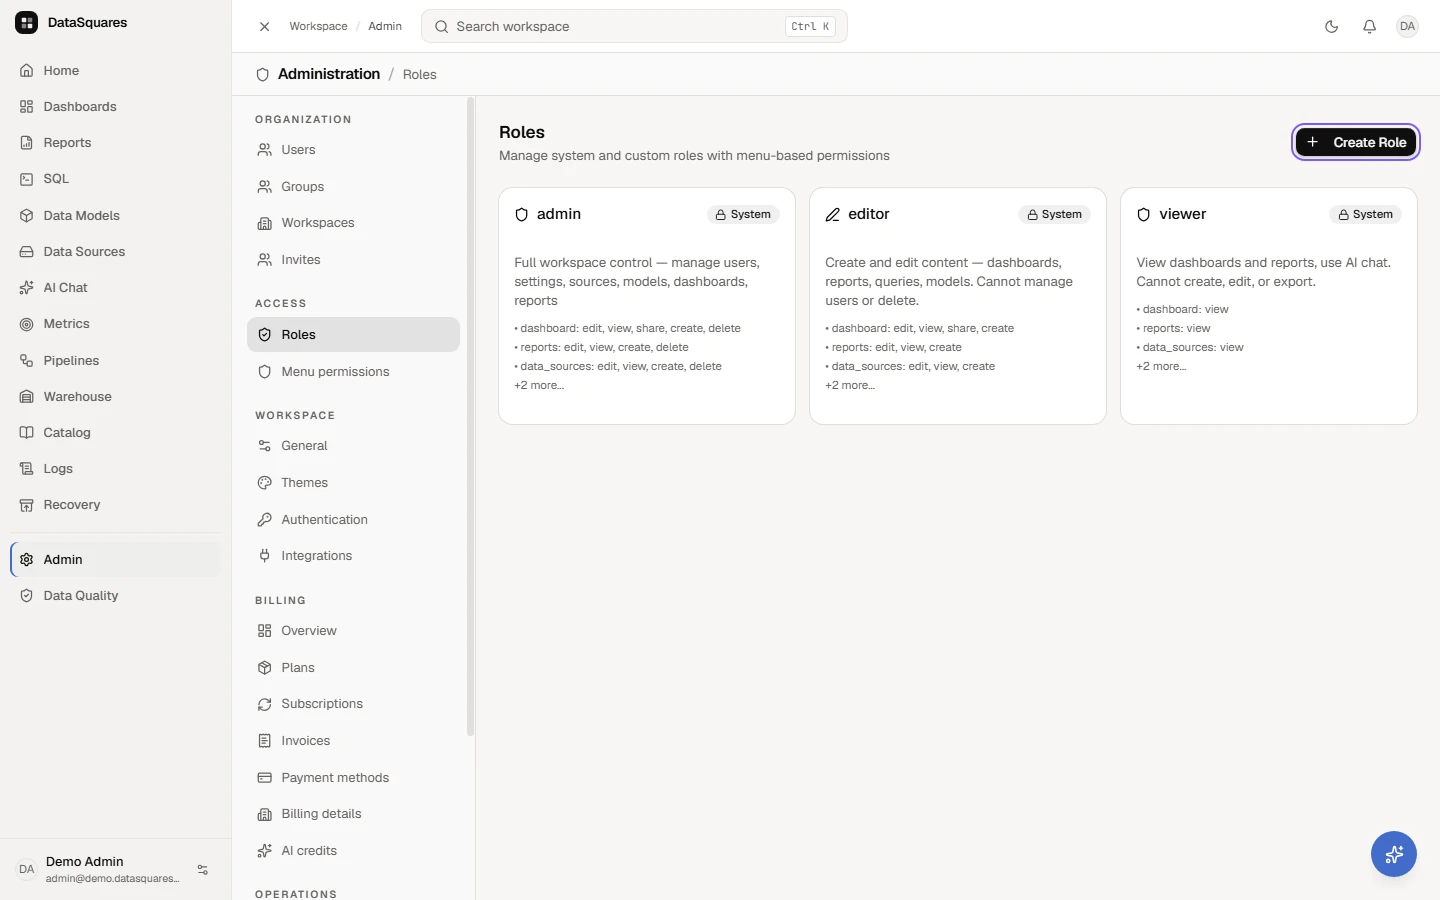
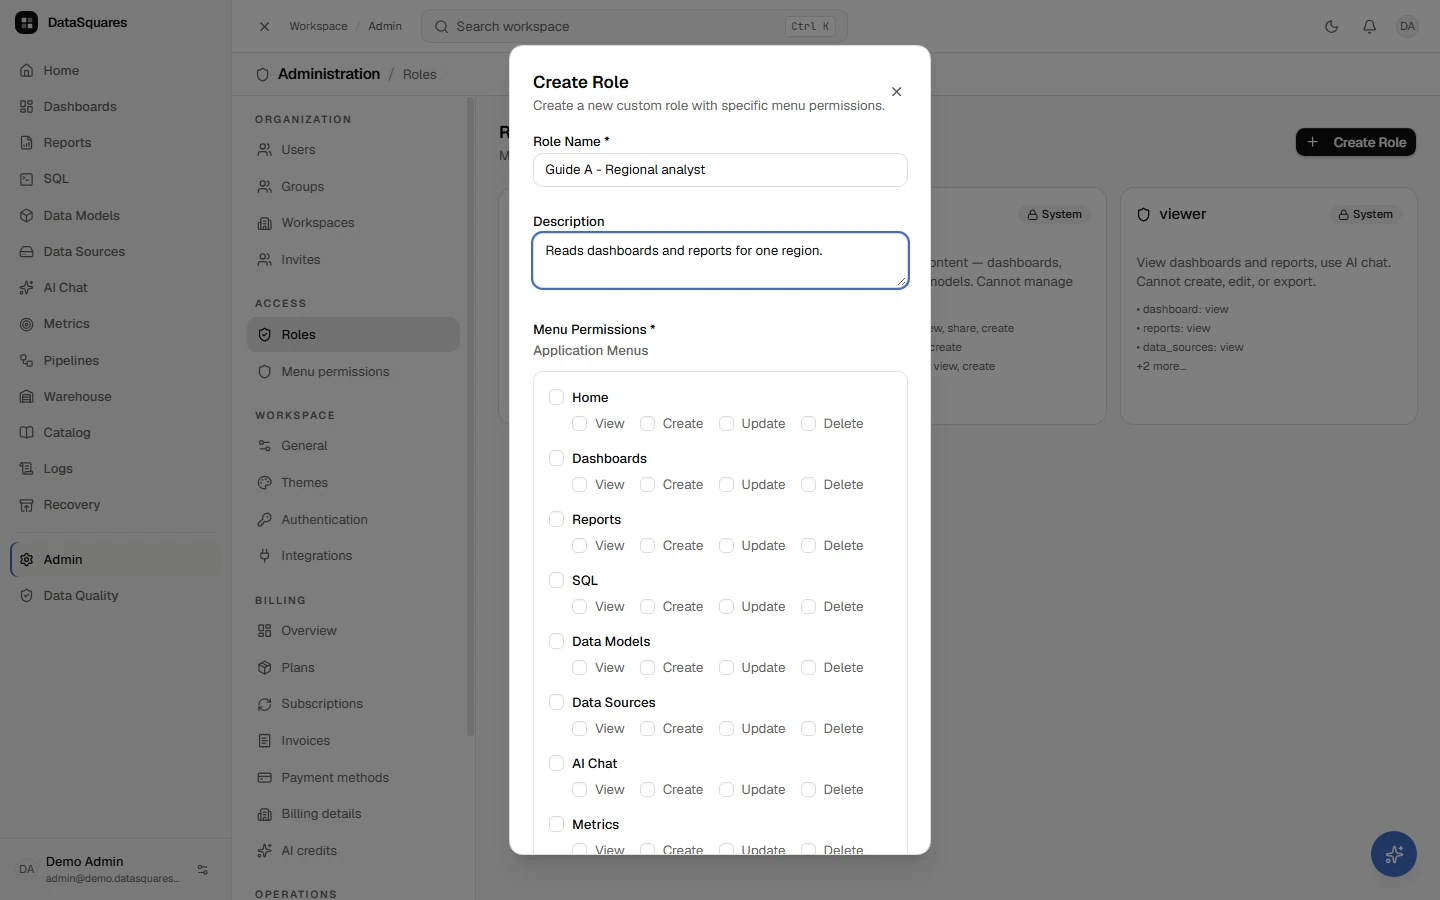
Choose Create Role. Give the role a name and a short description so other admins know what it is for.
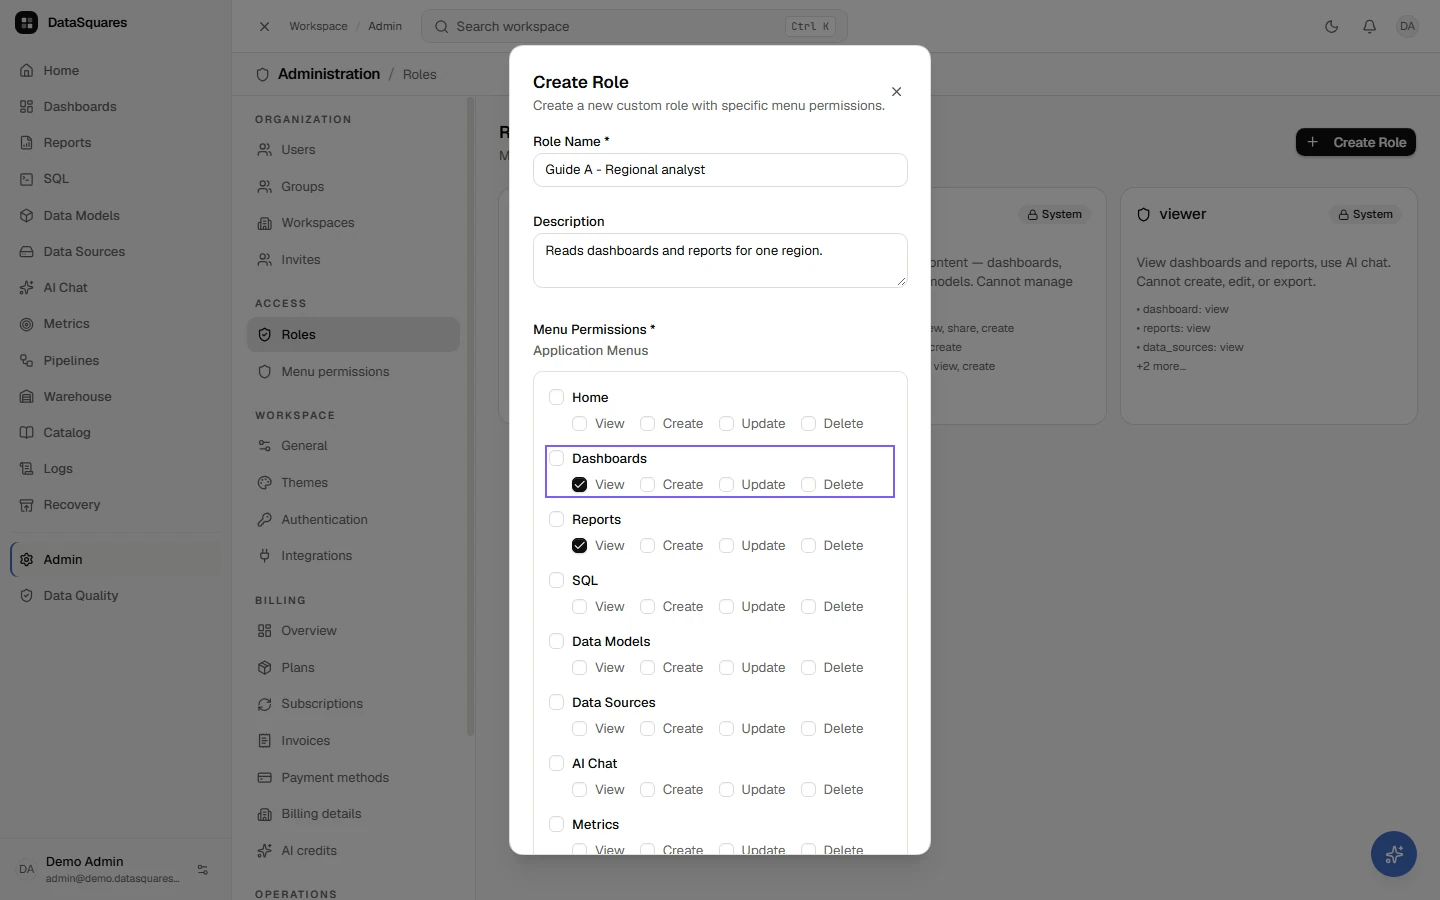
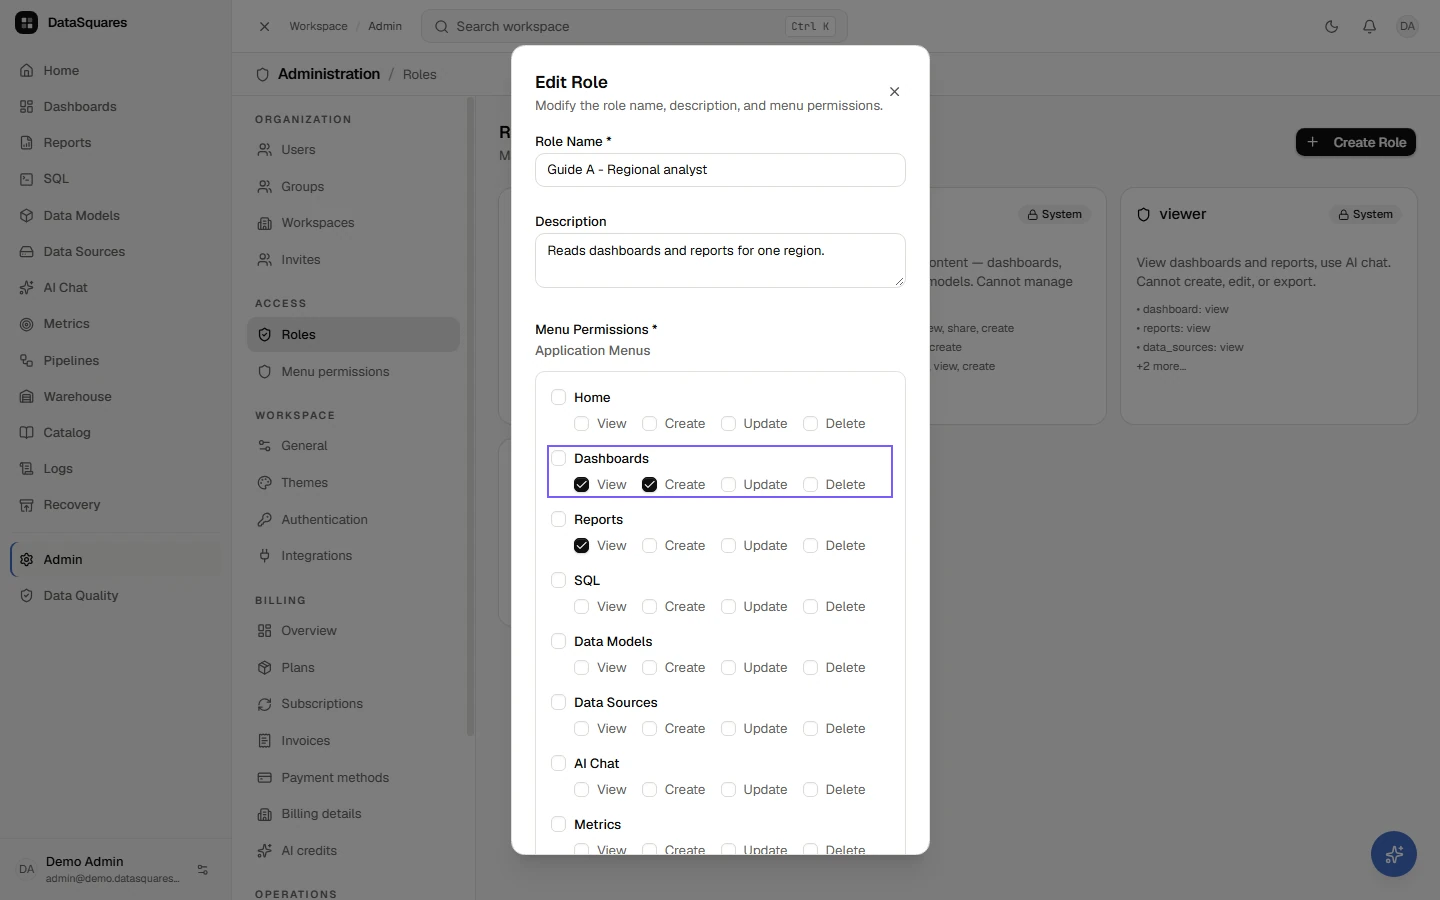
Tick what the role may do on each menu: View, Create, Update or Delete. This role can only view dashboards and reports.
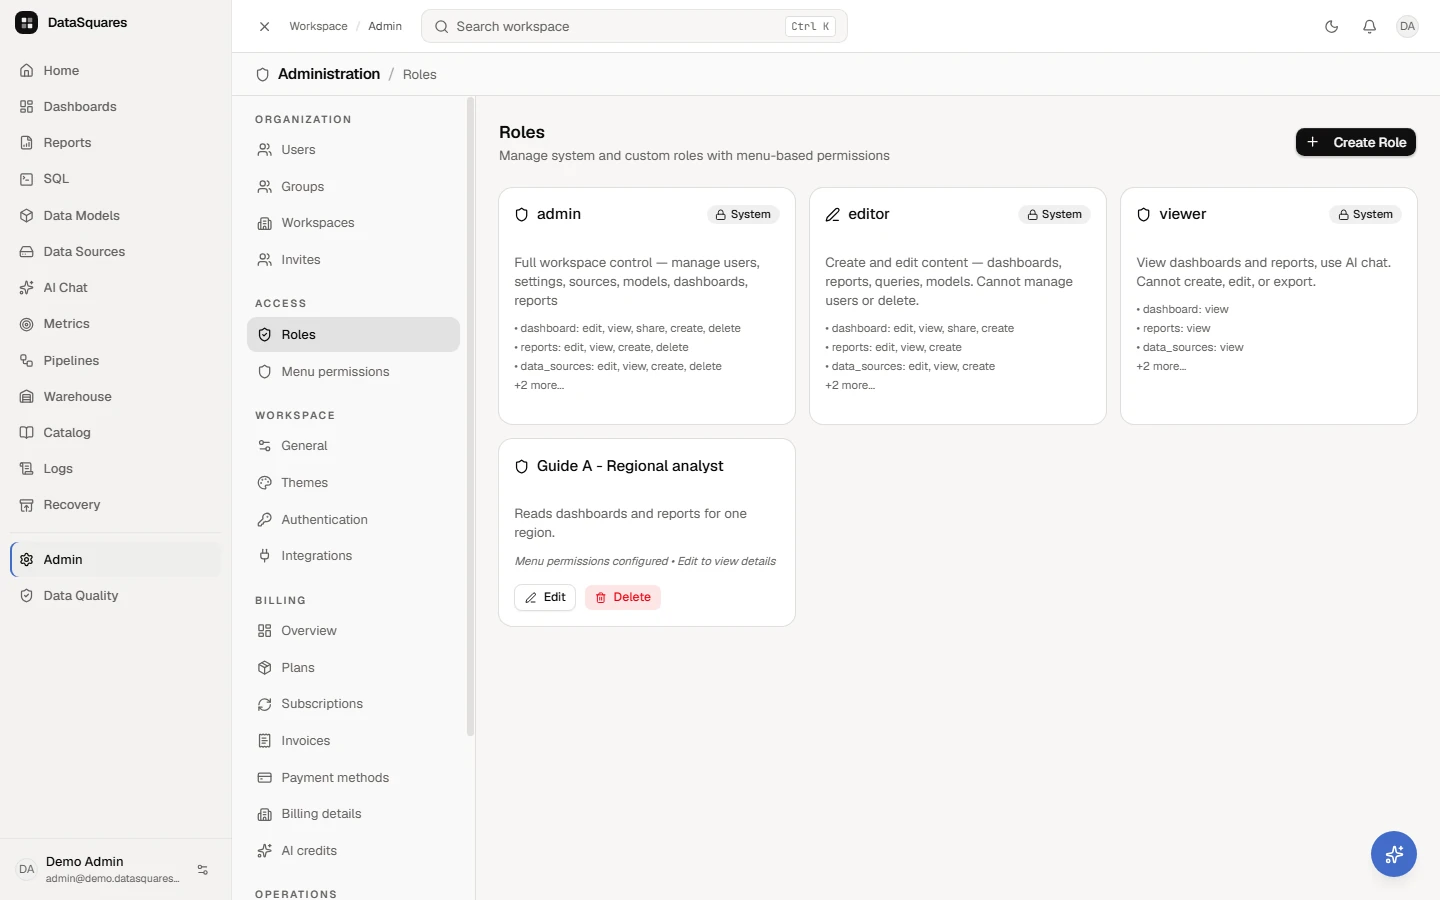
The role appears with the other roles. Custom roles have Edit and Delete buttons; system roles do not.
Choose Edit on the role card to change its permissions. Here the role is also allowed to create dashboards. Save your changes.
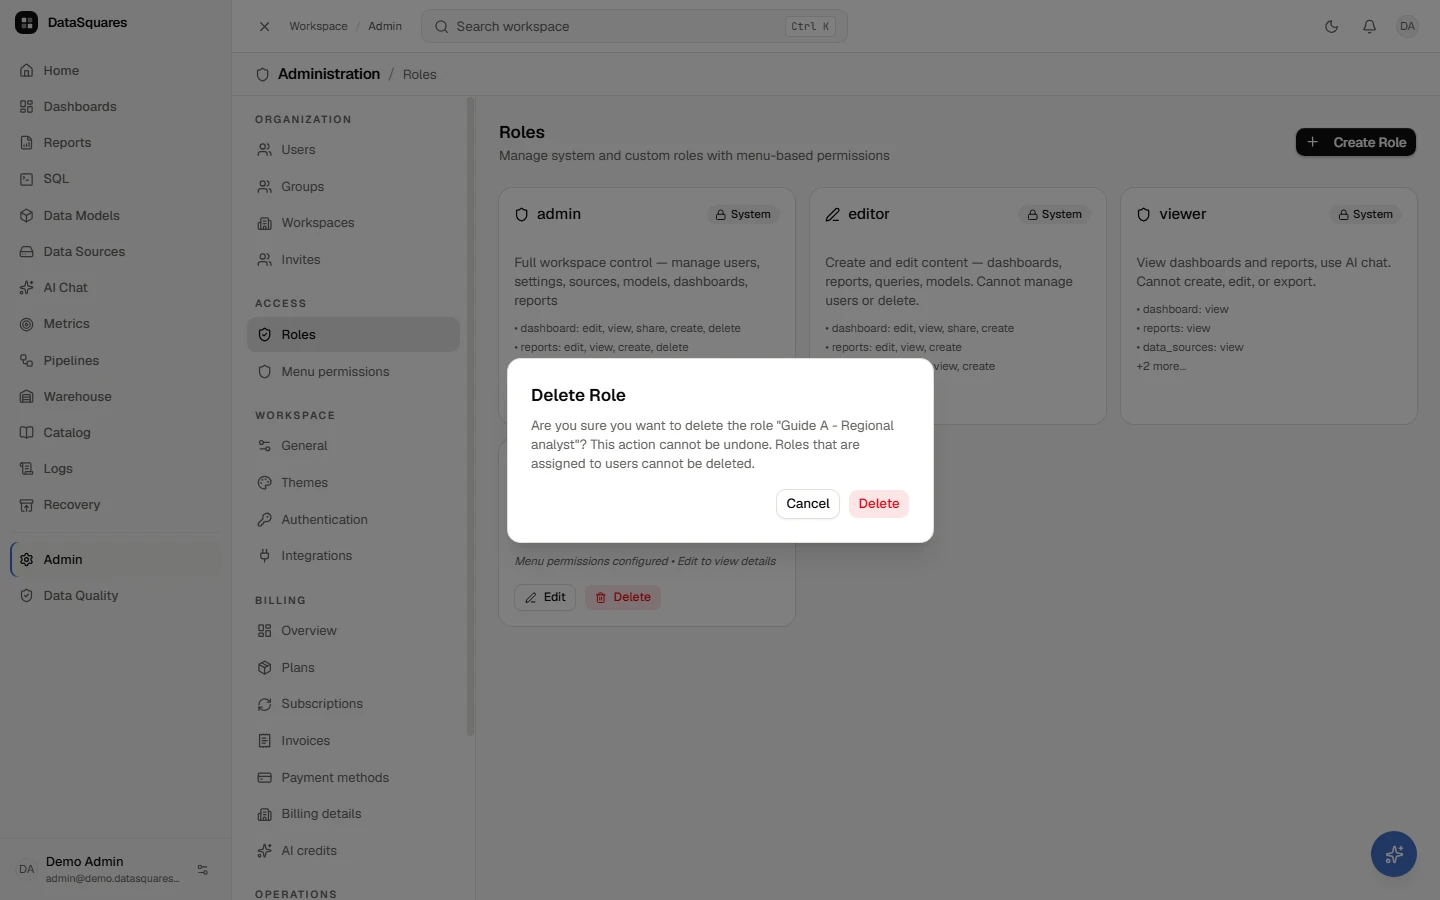
Choose Delete on the role to remove one you no longer need. A role that is still assigned to people cannot be deleted.
Walkthrough: control the navigation
Section titled “Walkthrough: control the navigation”Add an entry to the menu tree and relabel it for one role. Menu entries decide what people see; roles decide what they may open. The pictures show a private server. On the hosted service the menu is shared by every company, so the tree can’t be changed and steps 2 and 3 don’t apply; relabelling entries for one of your company’s own roles, the last two, works the same. See Menu builder on the hosted service.
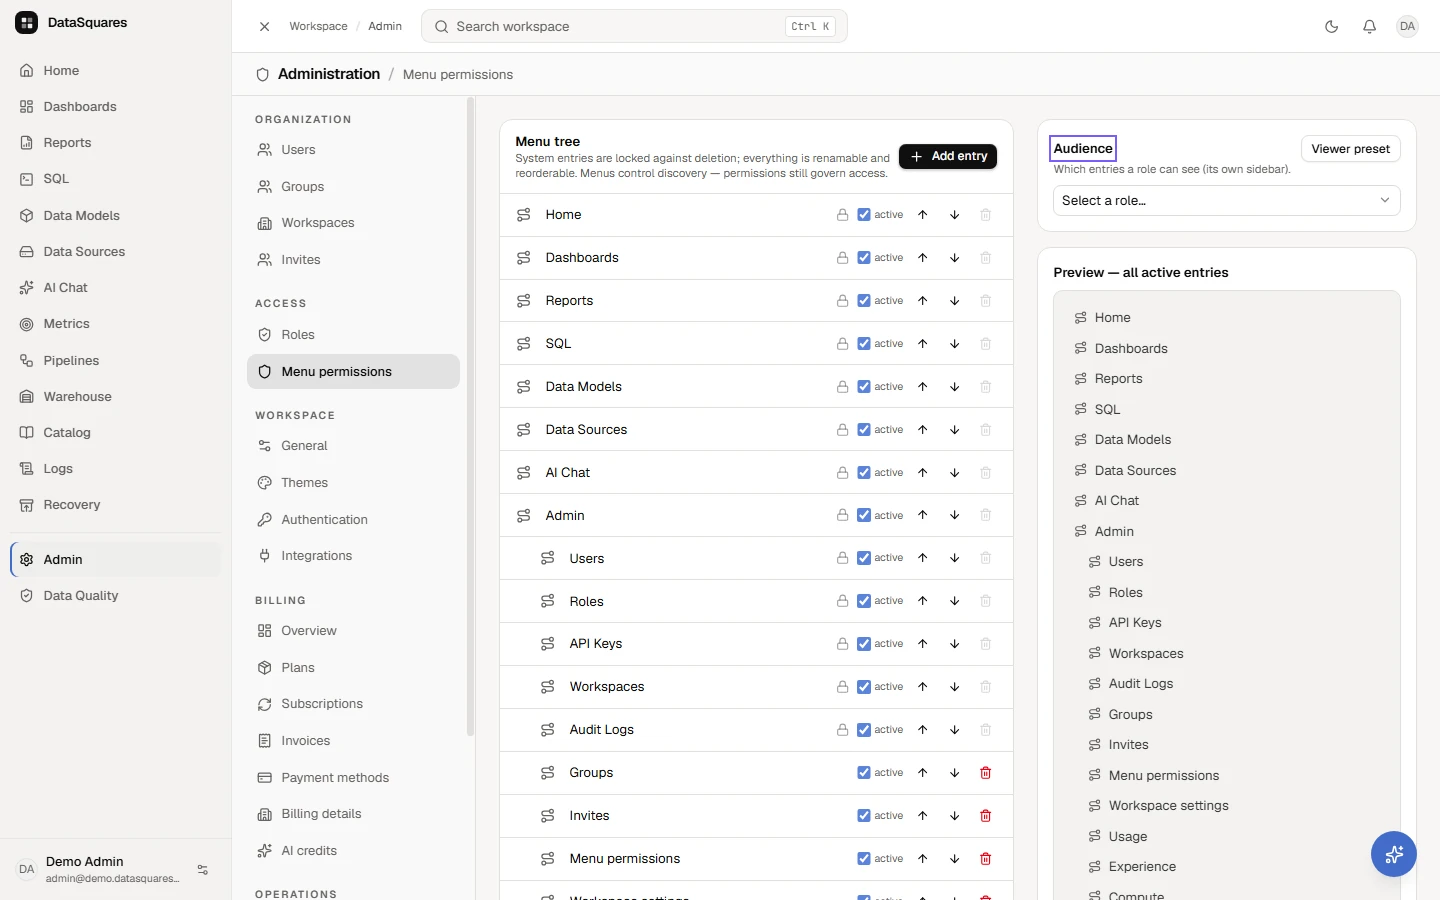
Open Admin, then Menu permissions. The menu tree on the left is the navigation people see. Audience on the right chooses which role you are shaping.
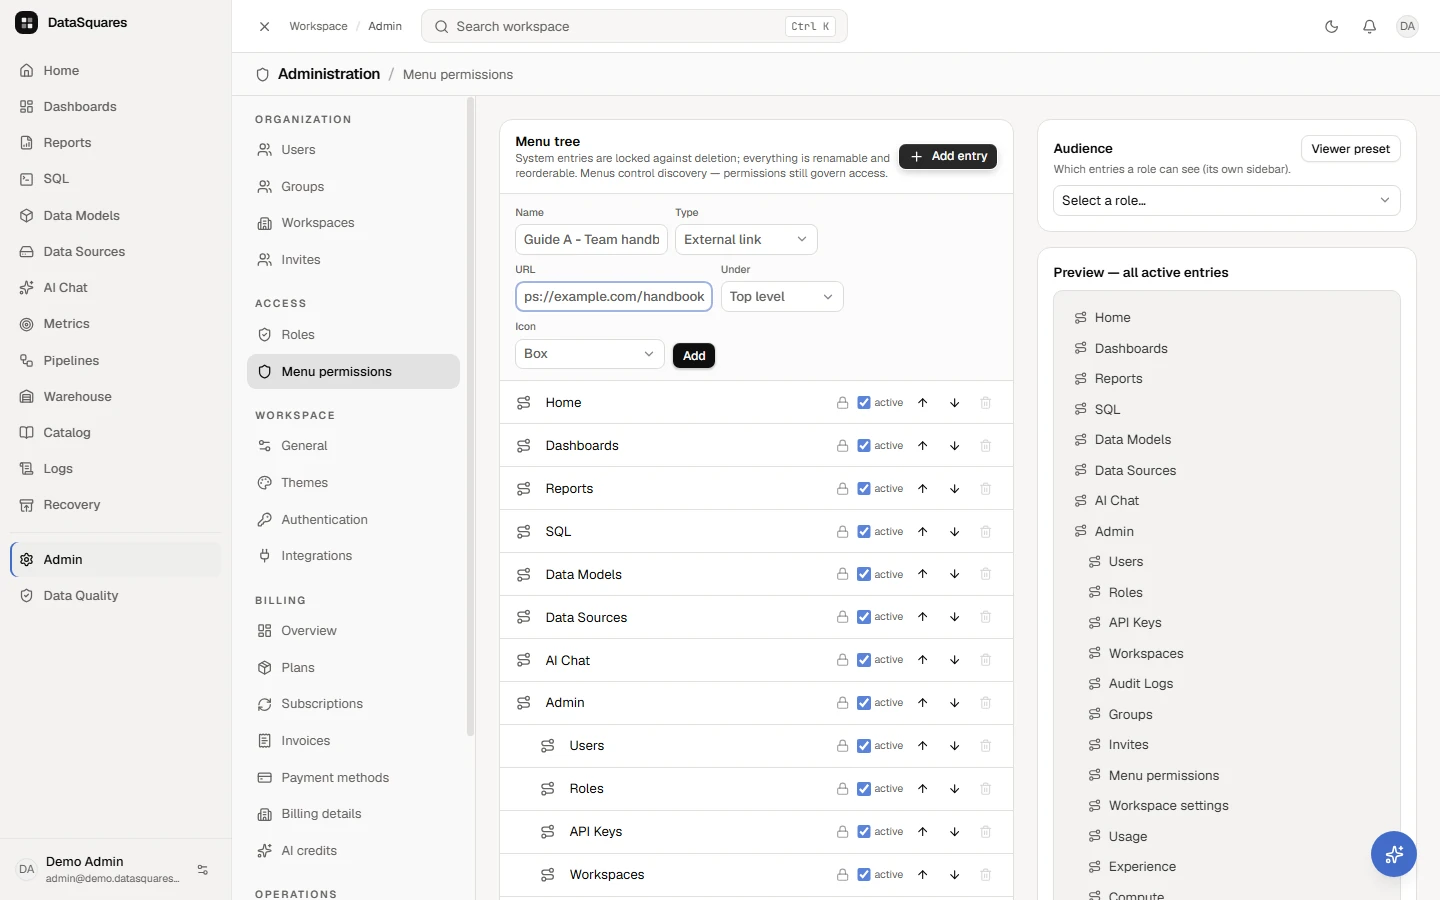
Choose Add entry. Name it and pick what it opens: an app page, a dashboard, a report, an external link or a section header. You can also choose where it sits in the tree.
The new entry joins the tree. Use the arrows to reorder it, the tick to show or hide it, and the bin to remove it. Entries marked with a lock are built in and cannot be deleted.
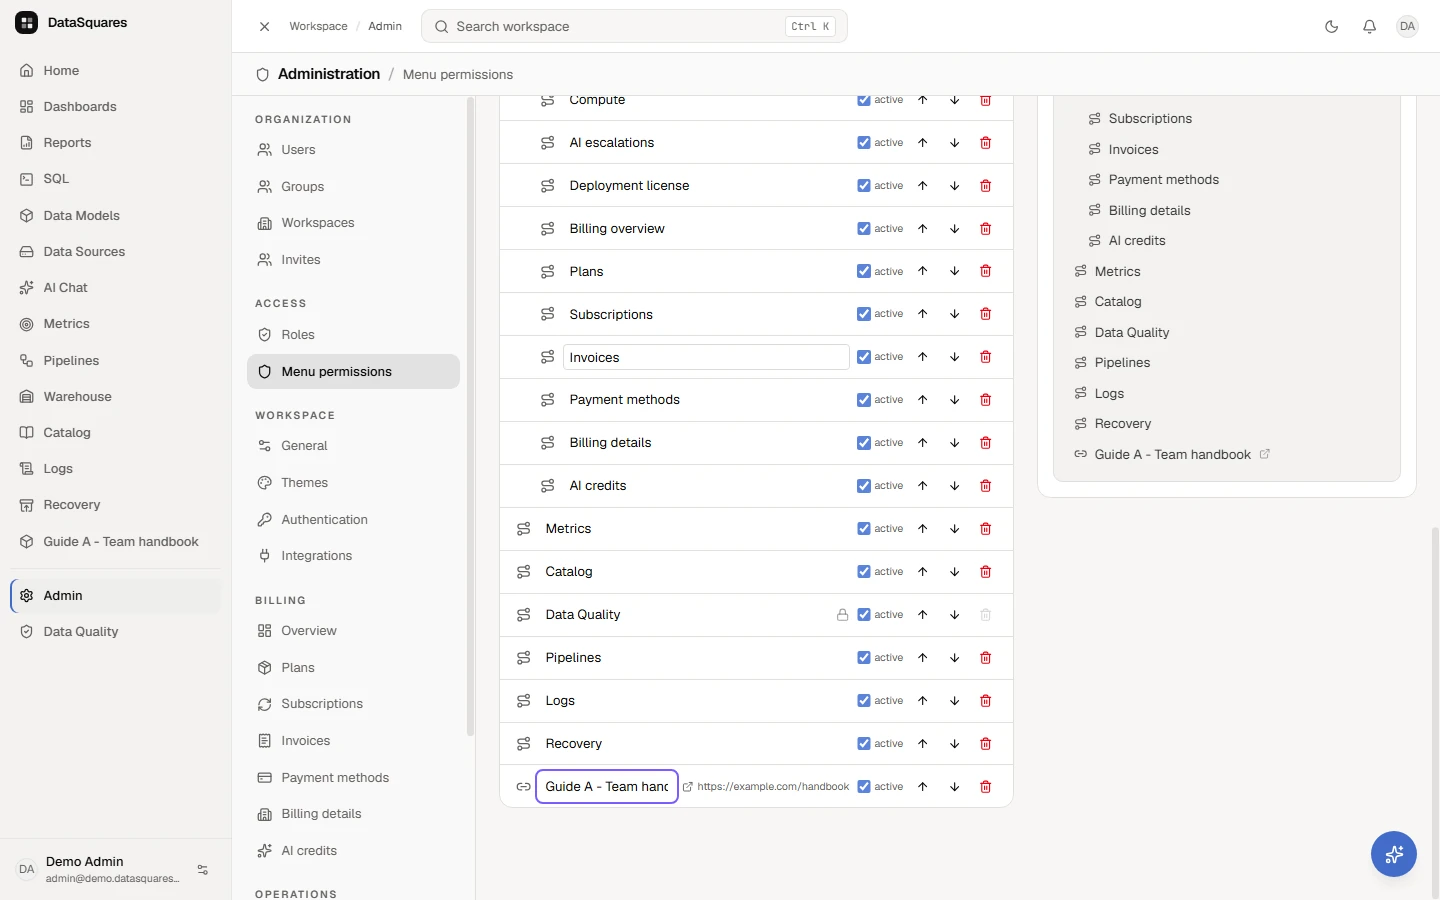
Under Audience, select a role to shape the navigation for that role. Every entry has a Relabel box, so one entry can carry a different name for that role.
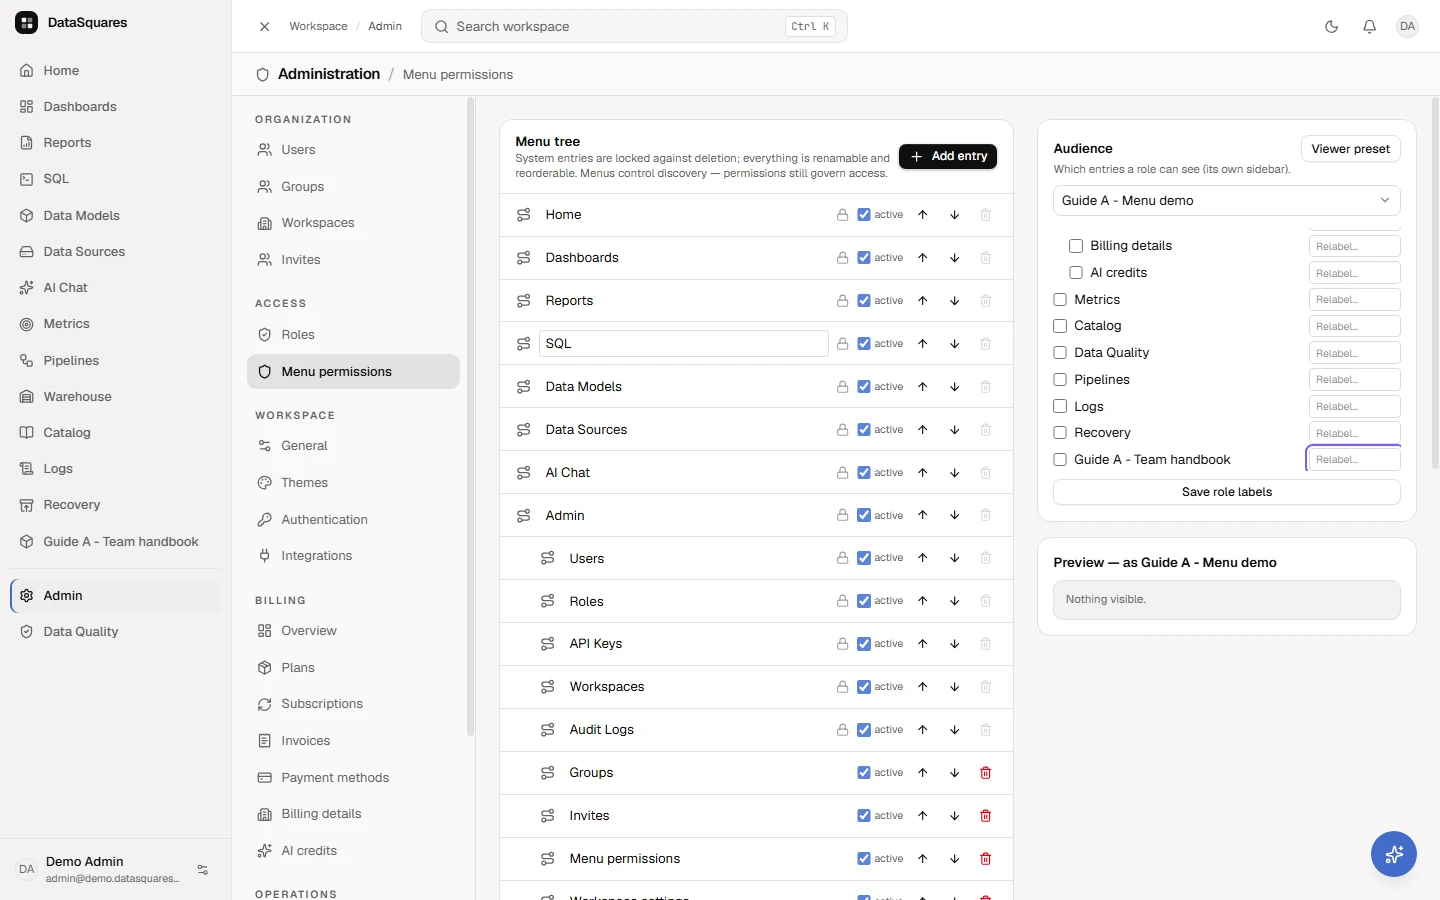
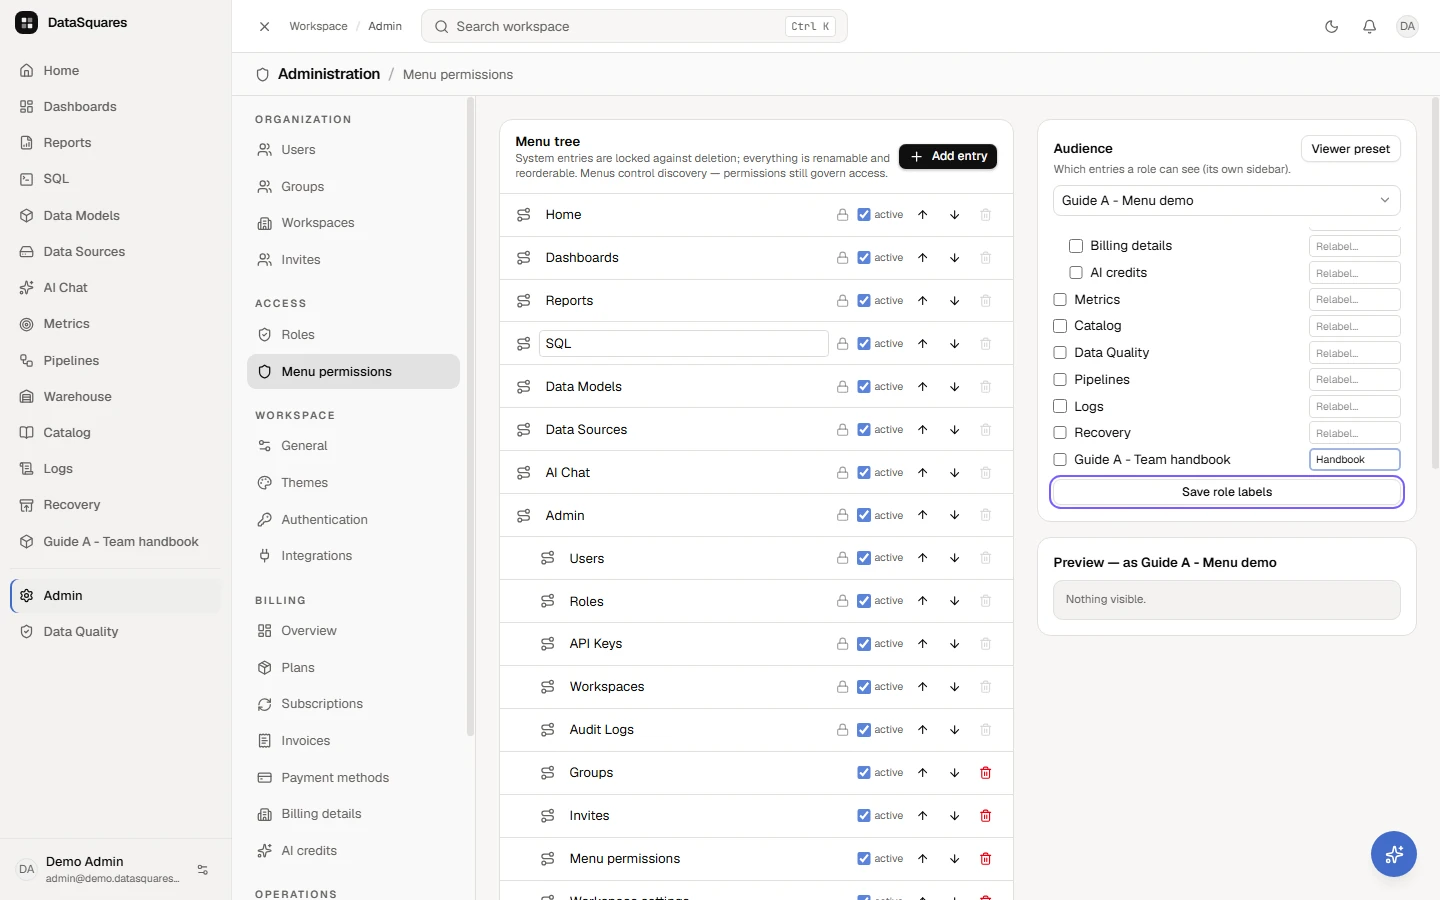
Type a label in the Relabel box to show the entry under a different name to this role only, then choose Save role labels.
Groups
Section titled “Groups”The Groups tab (/admin/groups) organizes members into logical teams (e.g. Finance, Marketing Analytics, Data Engineering):
- Assign users to multiple groups.
- Manage team-level permissions and share dashboard collections or models with entire groups simultaneously.
Walkthrough: organise people into groups
Section titled “Walkthrough: organise people into groups”Create a group, add members, remove one and delete the group.
Open Admin, then Groups. A group is a named set of people you can grant access to as one.
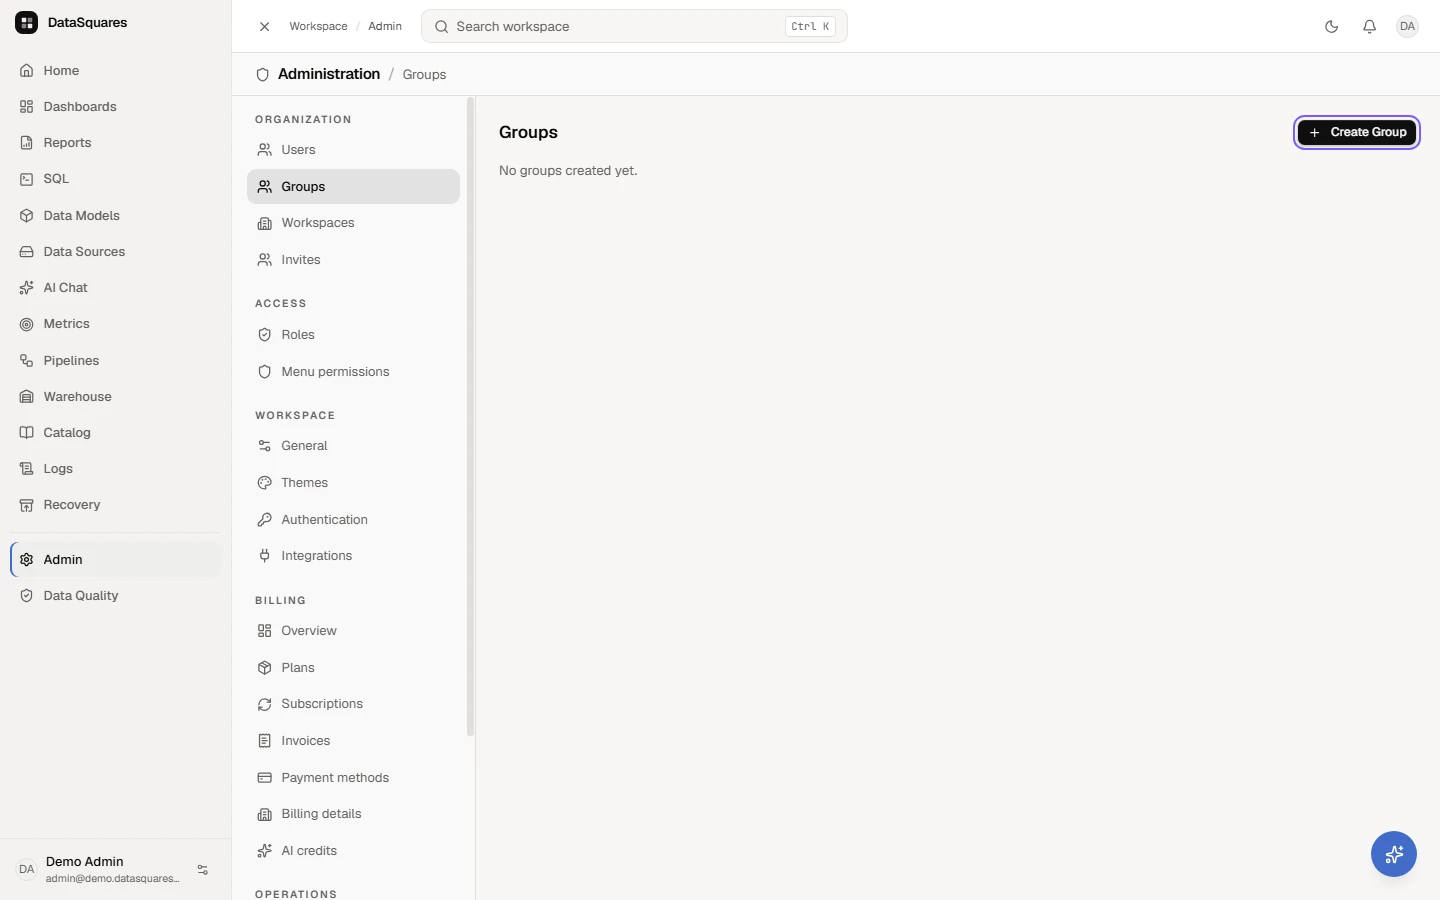
Choose Create Group, then give it a name and an optional description.
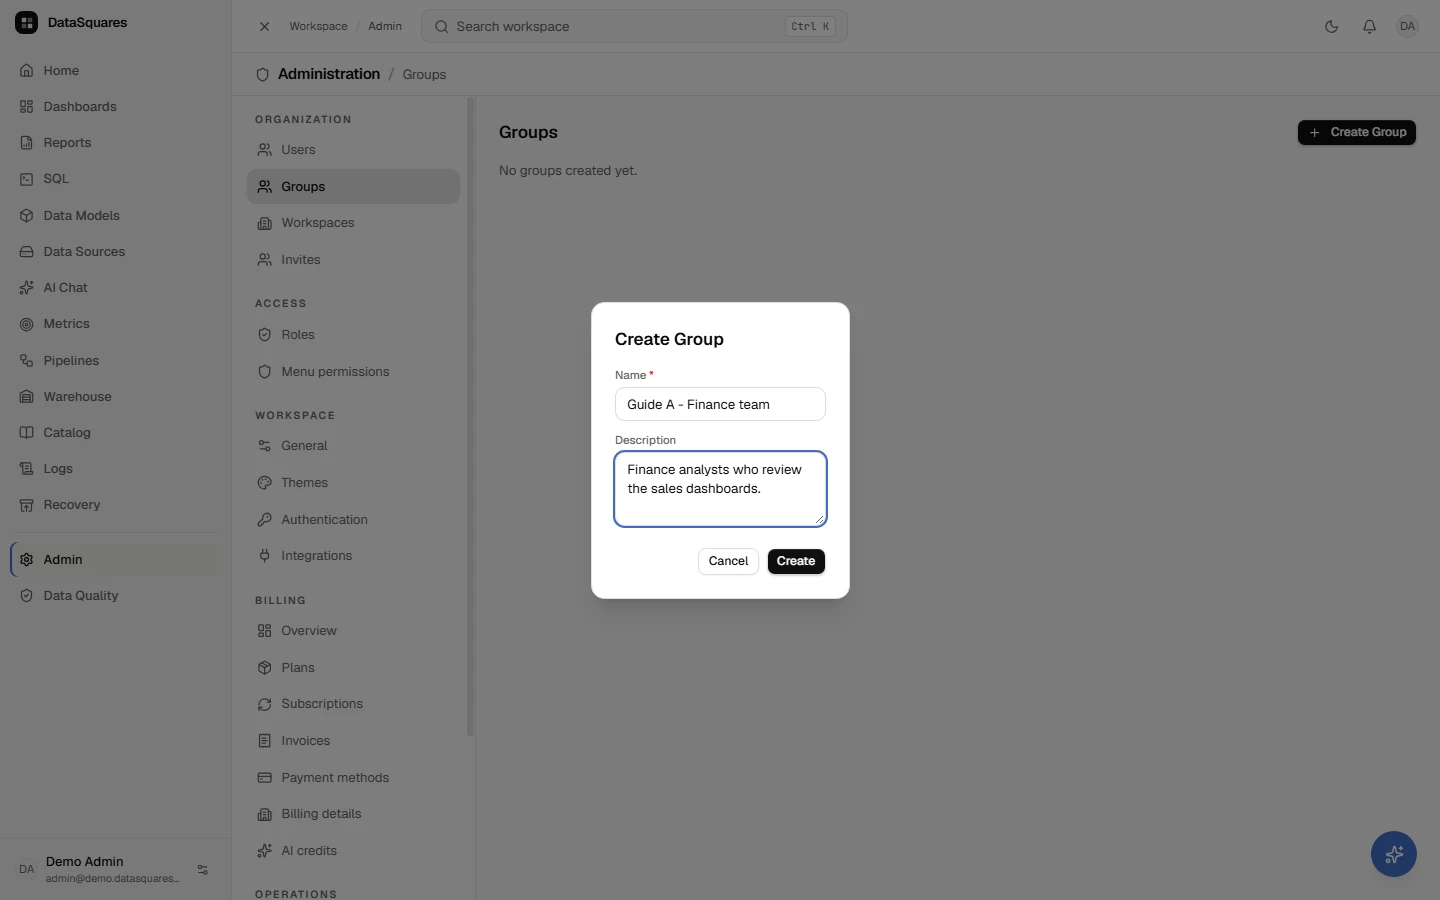
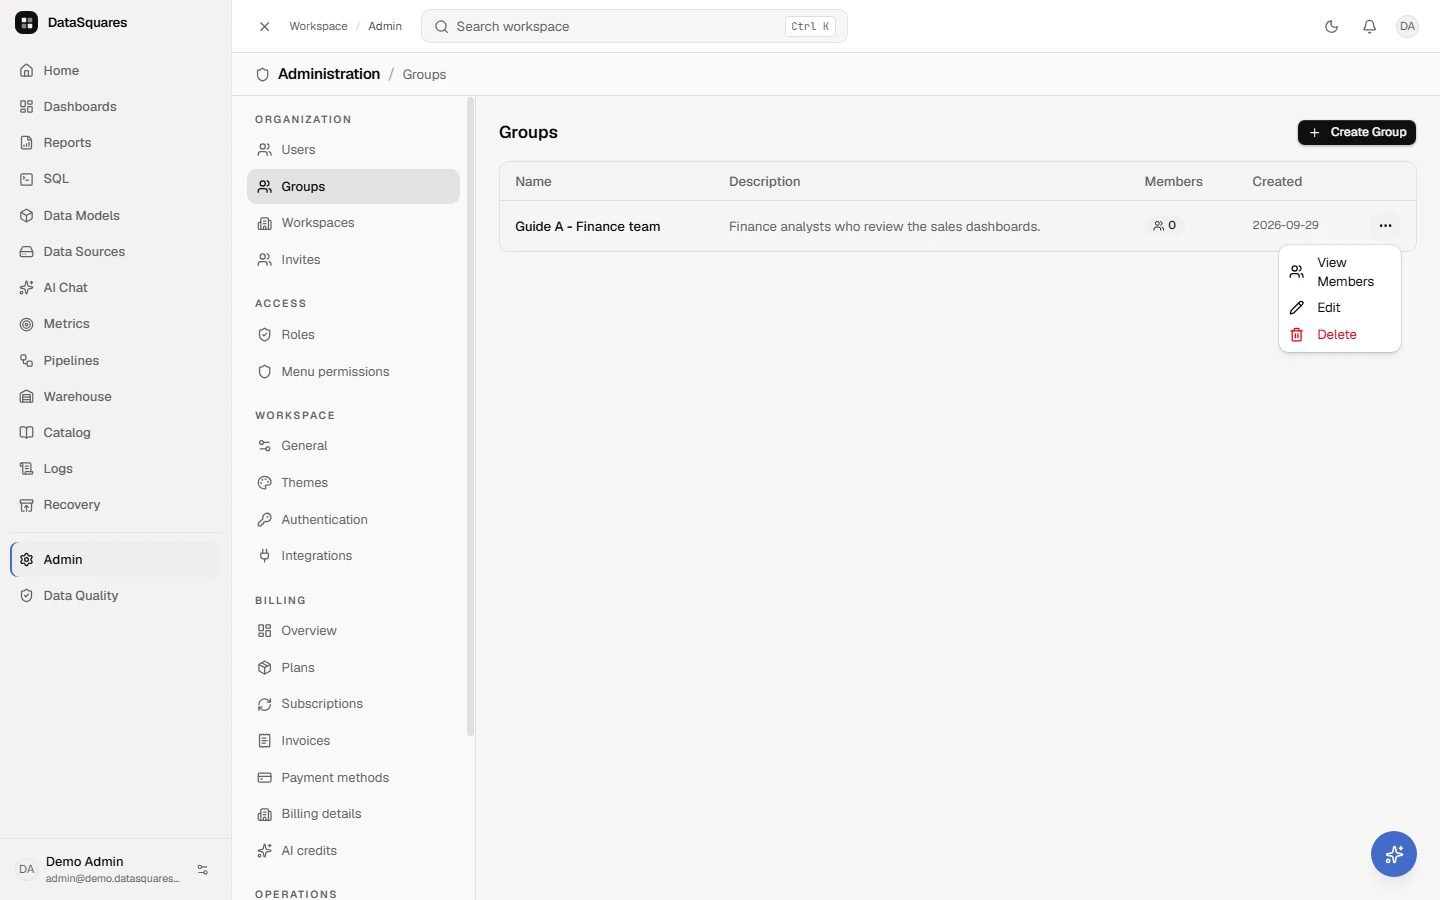
Open the Actions menu on the group and choose View Members. From there you can also edit or delete the group.
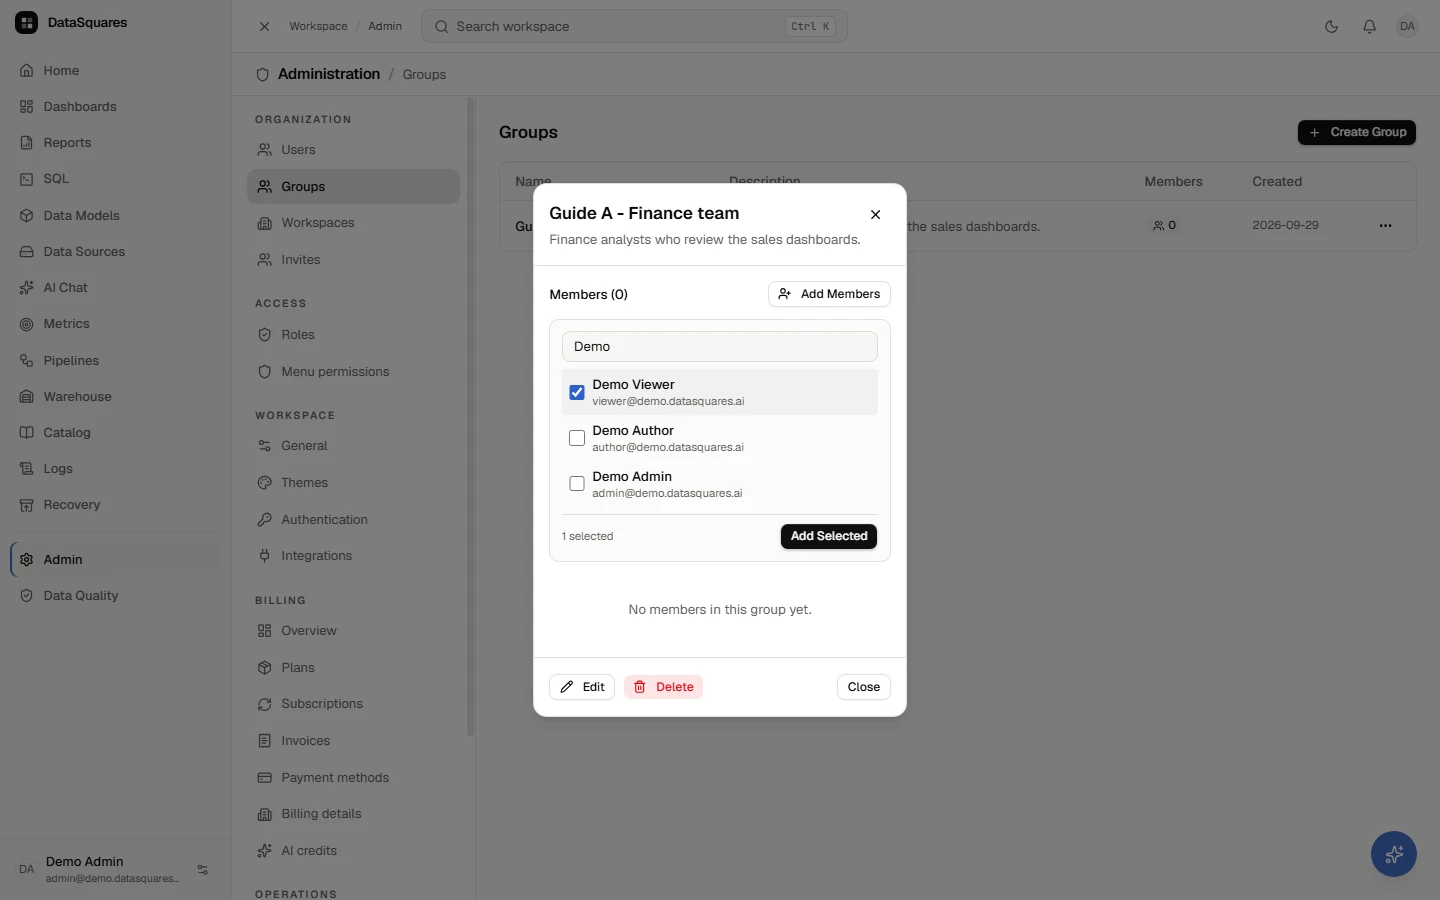
Choose Add Members, search for people and tick the ones to add.
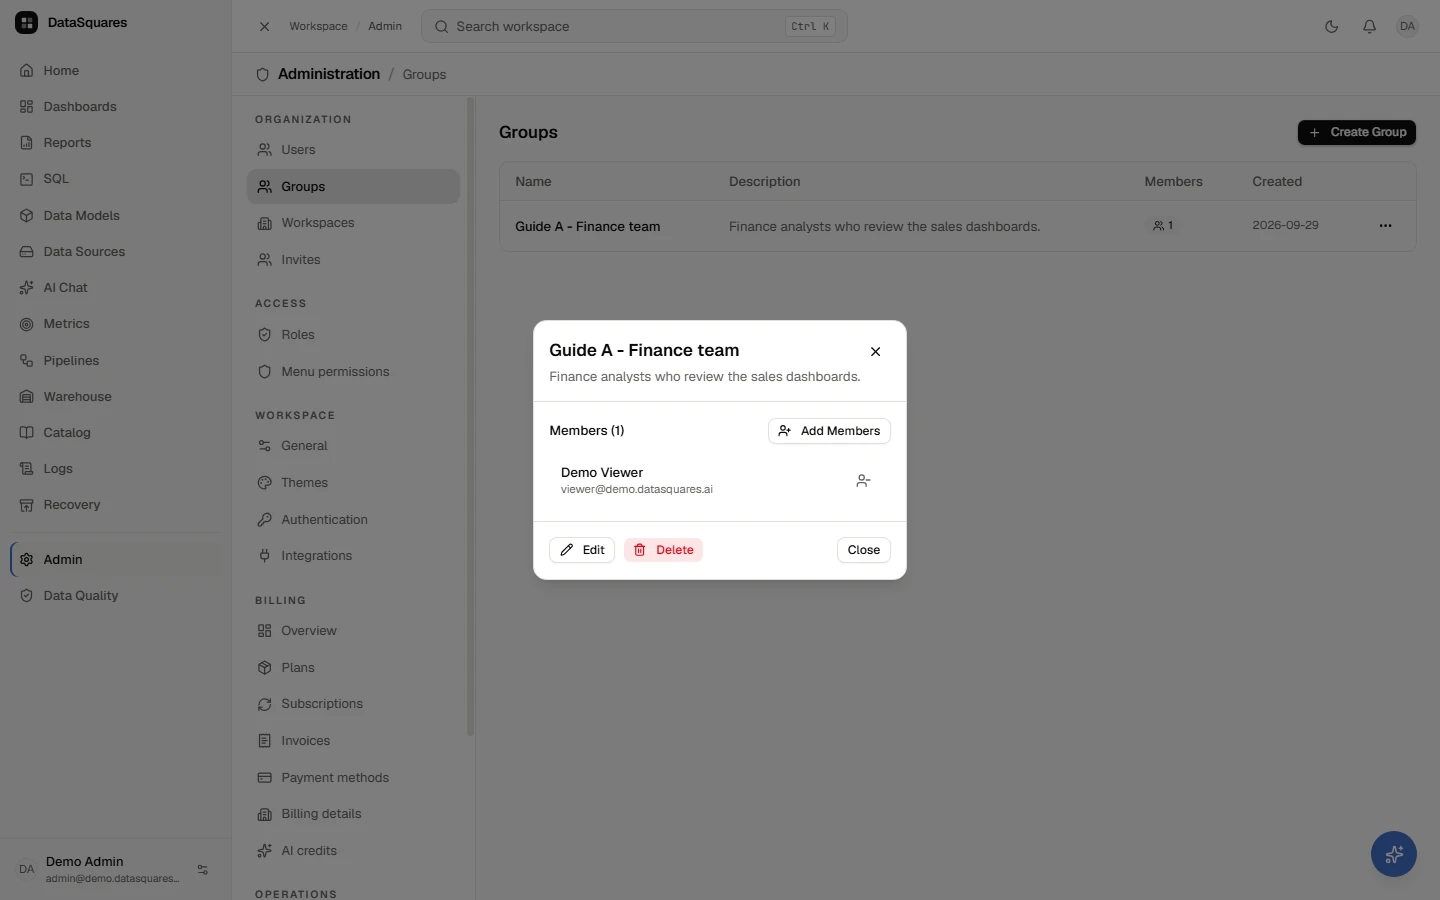
The group now lists its members. Use the remove button beside a name to take someone out again.
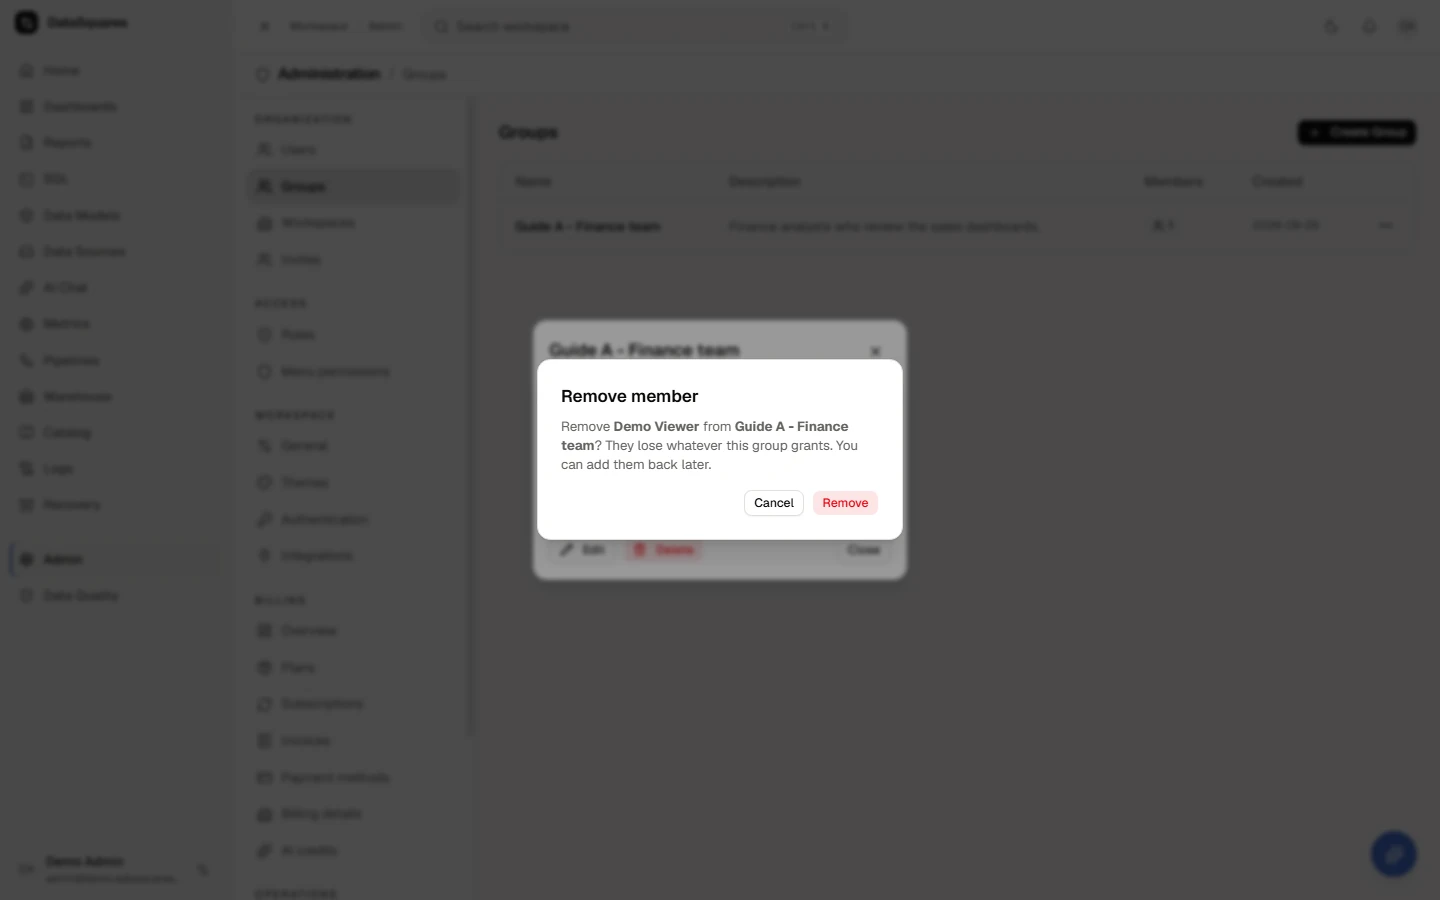
Removing a member asks you to confirm. They lose whatever the group grants, and you can add them back later.
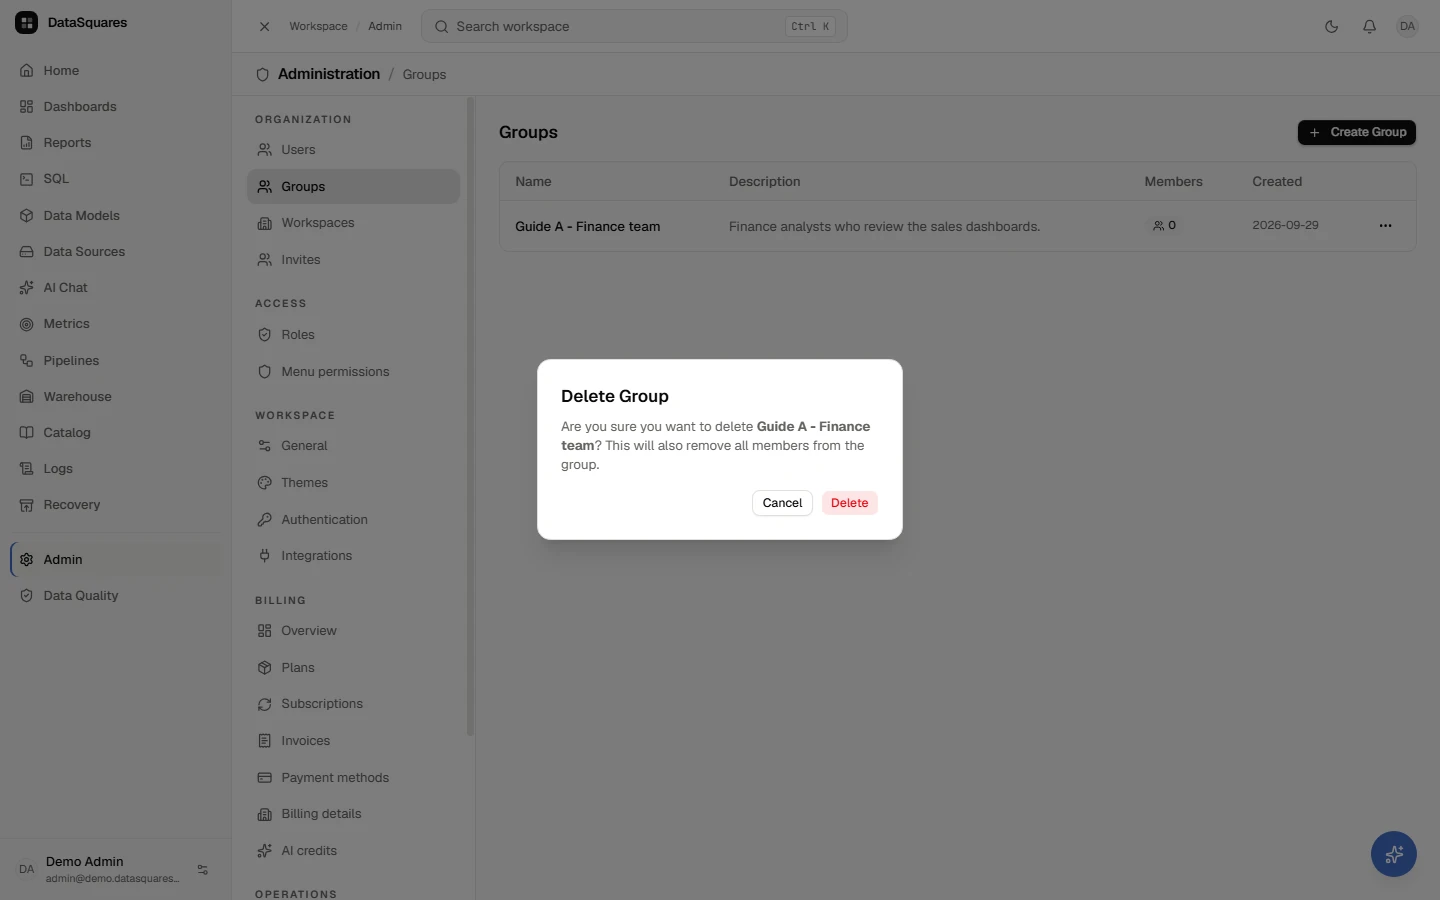
Choose Delete to remove the group itself. The people in it stay in the workspace.
Workspaces
Section titled “Workspaces”The Workspaces tab (/admin/workspaces) manages multi-workspace environments within an enterprise tenant:
- Isolate environments (e.g.
Production,Staging,Analytics Sandbox). - Manage workspace-level membership, quotas, and resource isolation.
Walkthrough: create a workspace
Section titled “Walkthrough: create a workspace”Create a workspace, add a member with a role, remove them and delete the workspace.
Open Admin, then Workspaces. Each workspace keeps its own dashboards, data sources and members.
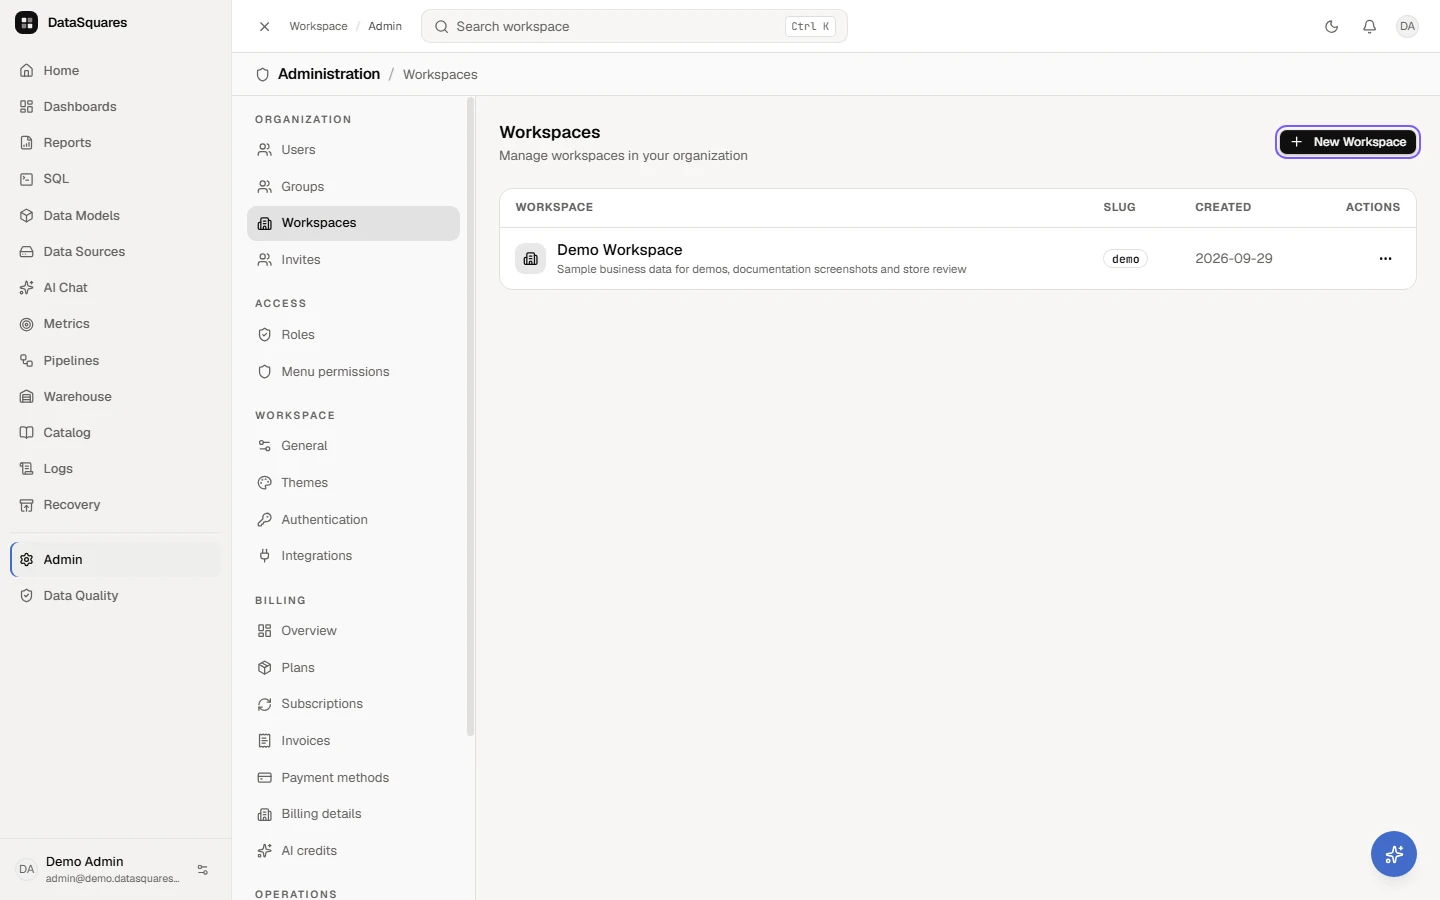
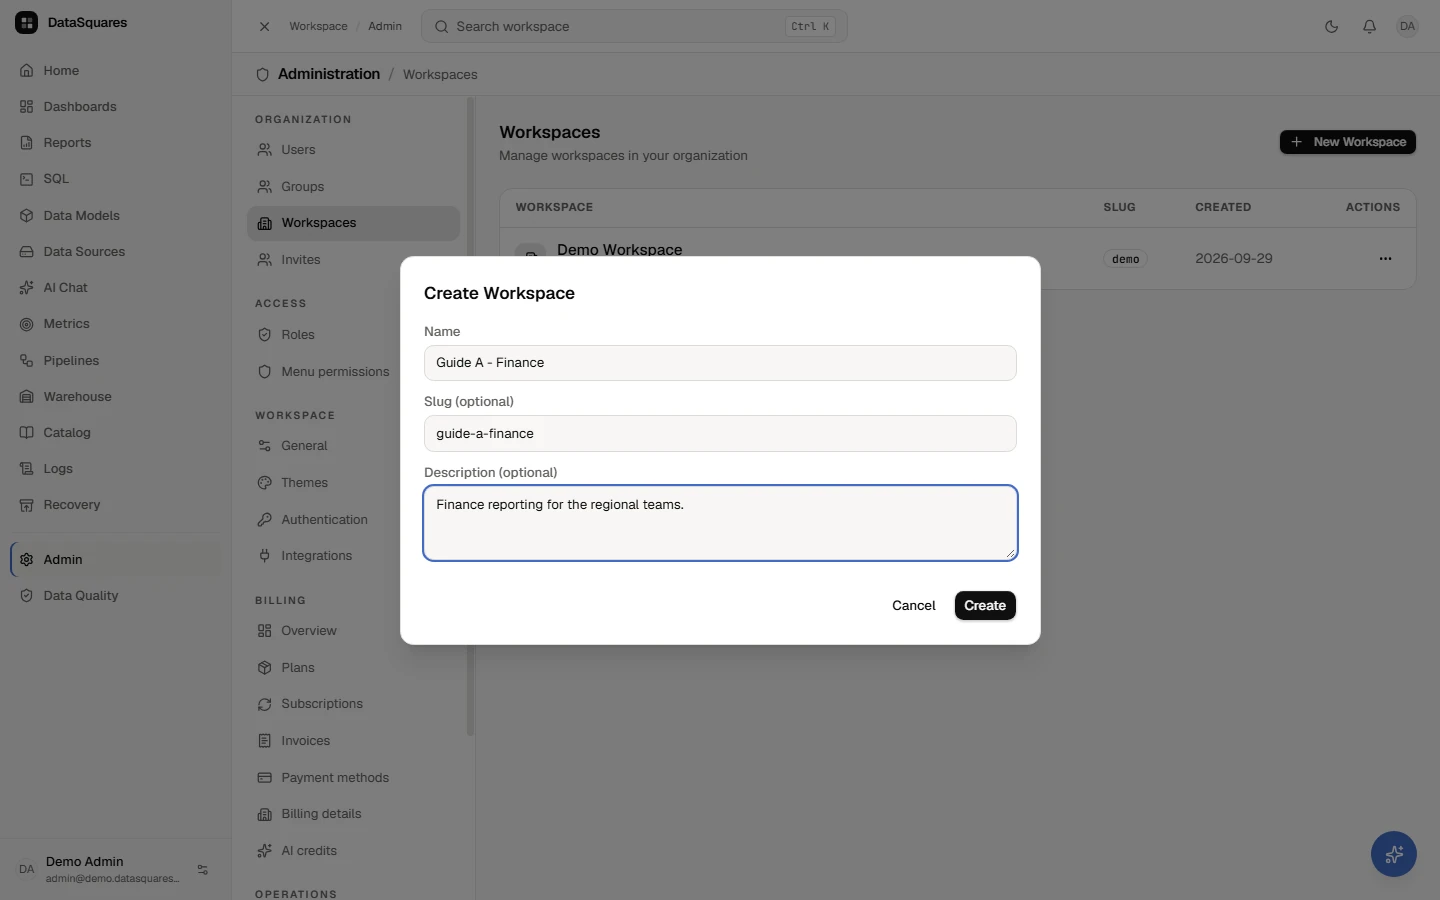
Choose New Workspace. Enter a name, an optional slug for its address, and a short description, then create it.
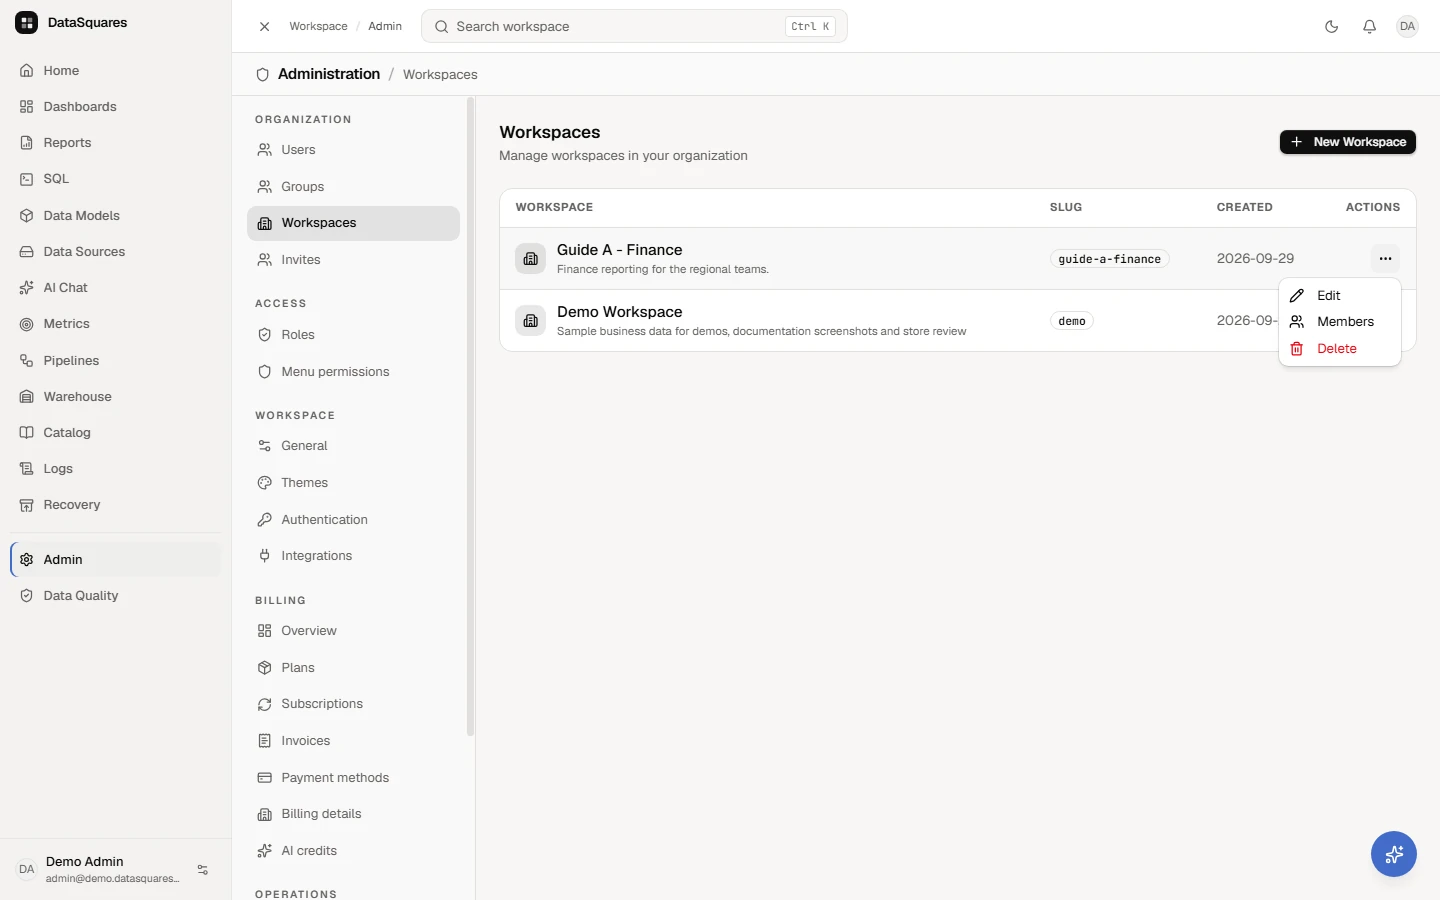
Open the Actions menu on the workspace and choose Members. You can also edit or delete it here.
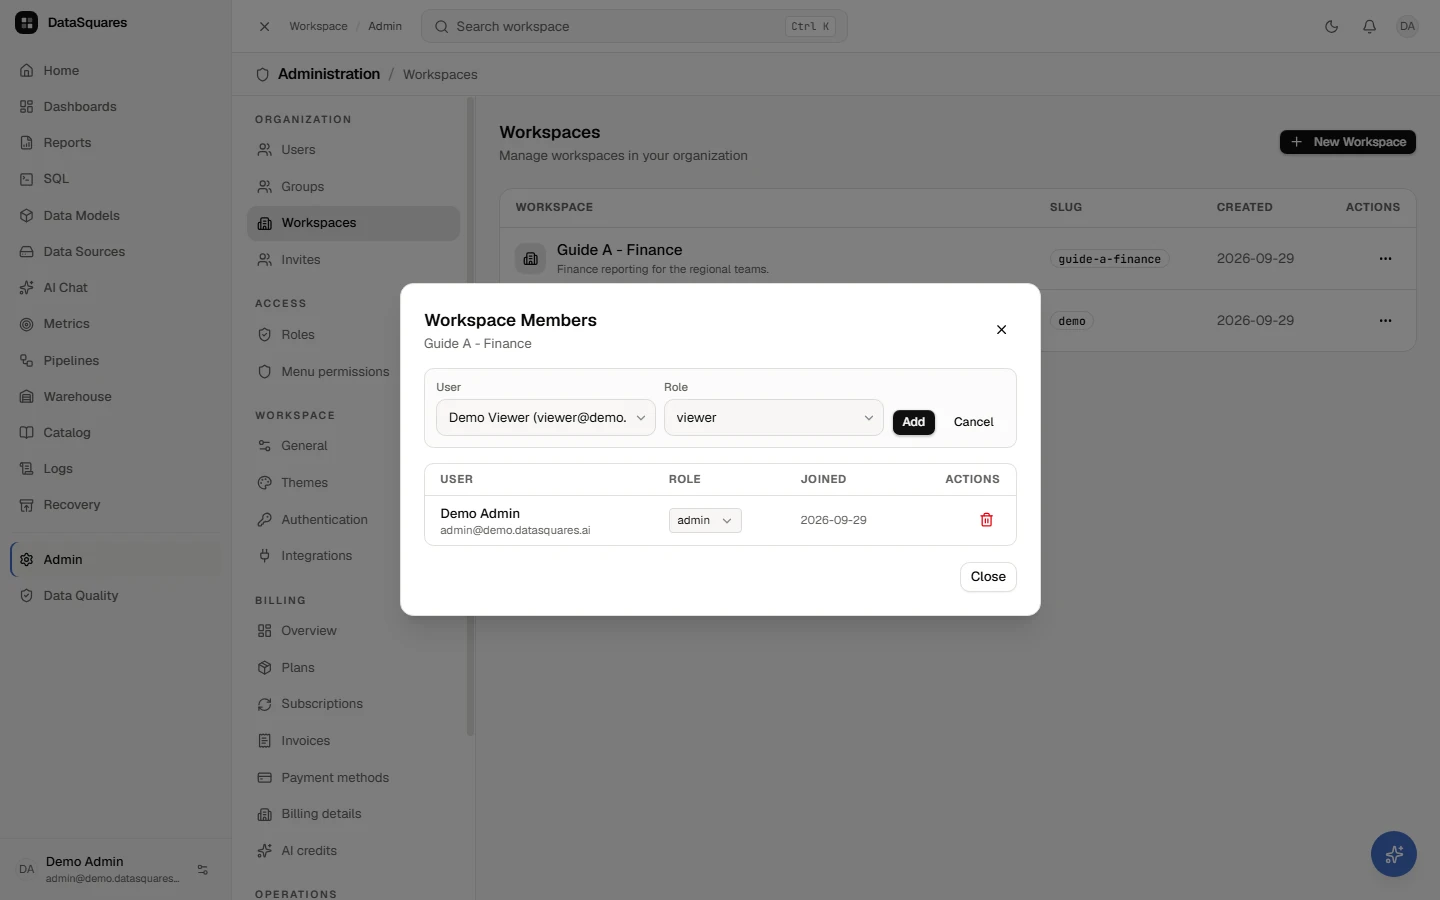
Choose Add Member, pick the person and the role they have in this workspace, then choose Add.
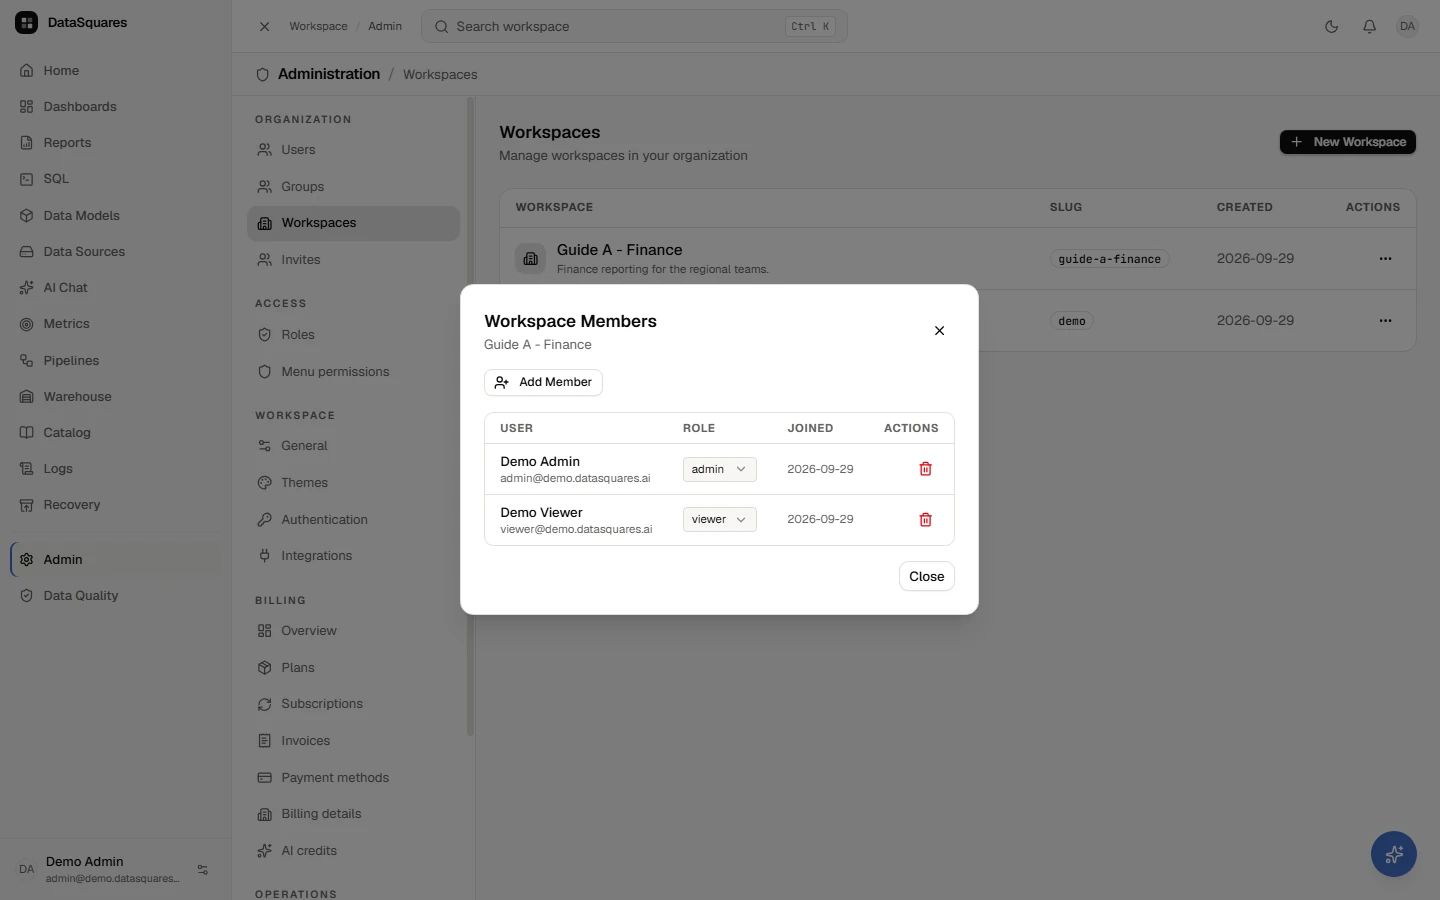
The member list shows each person, their role and when they joined. Use the remove button to take someone out.
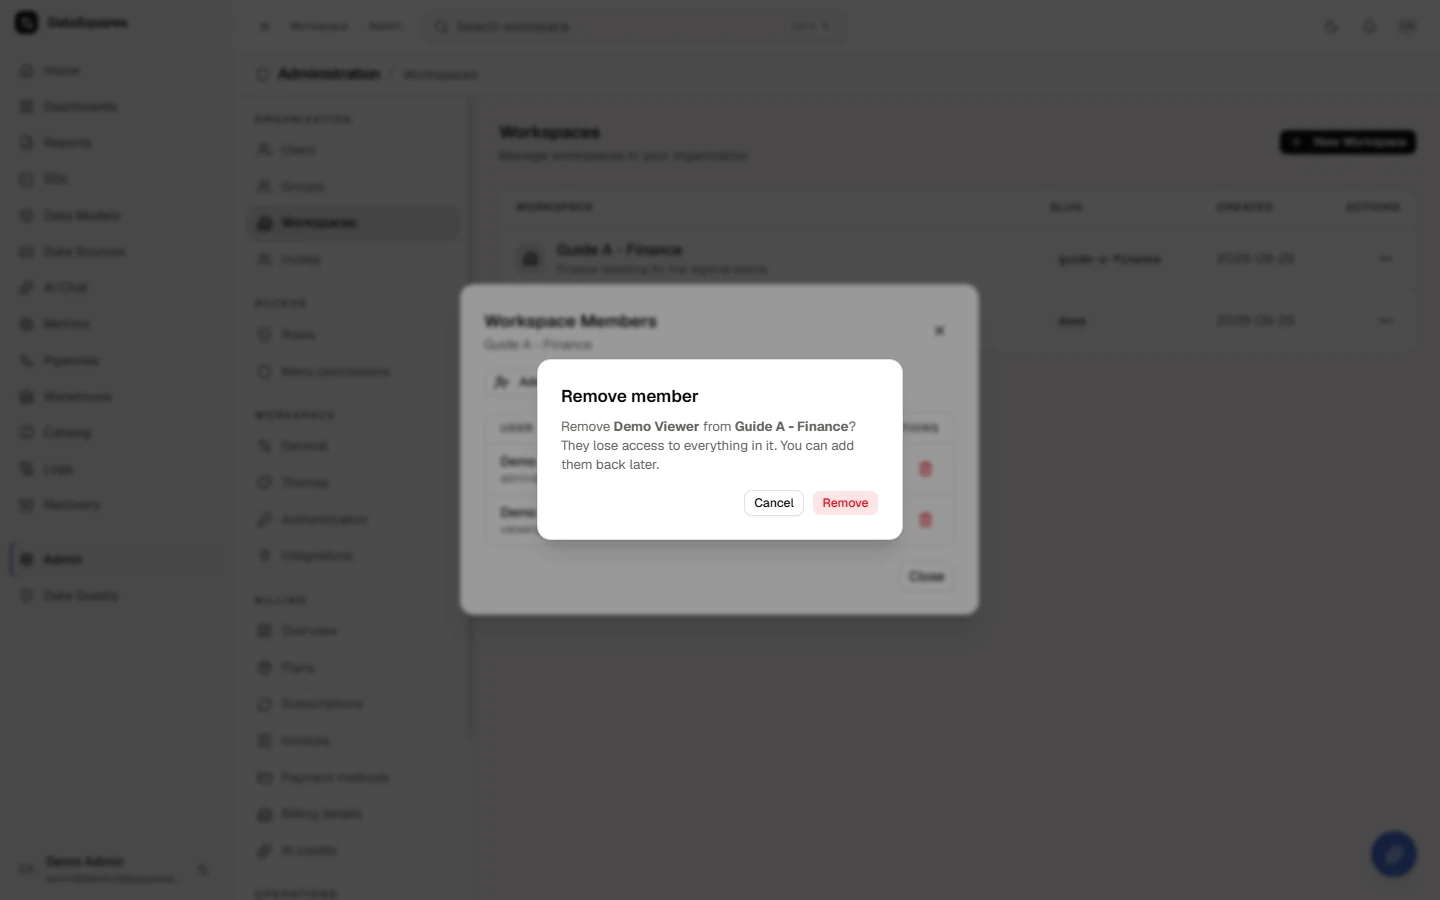
Removing a member asks you to confirm. They lose access to everything in the workspace.
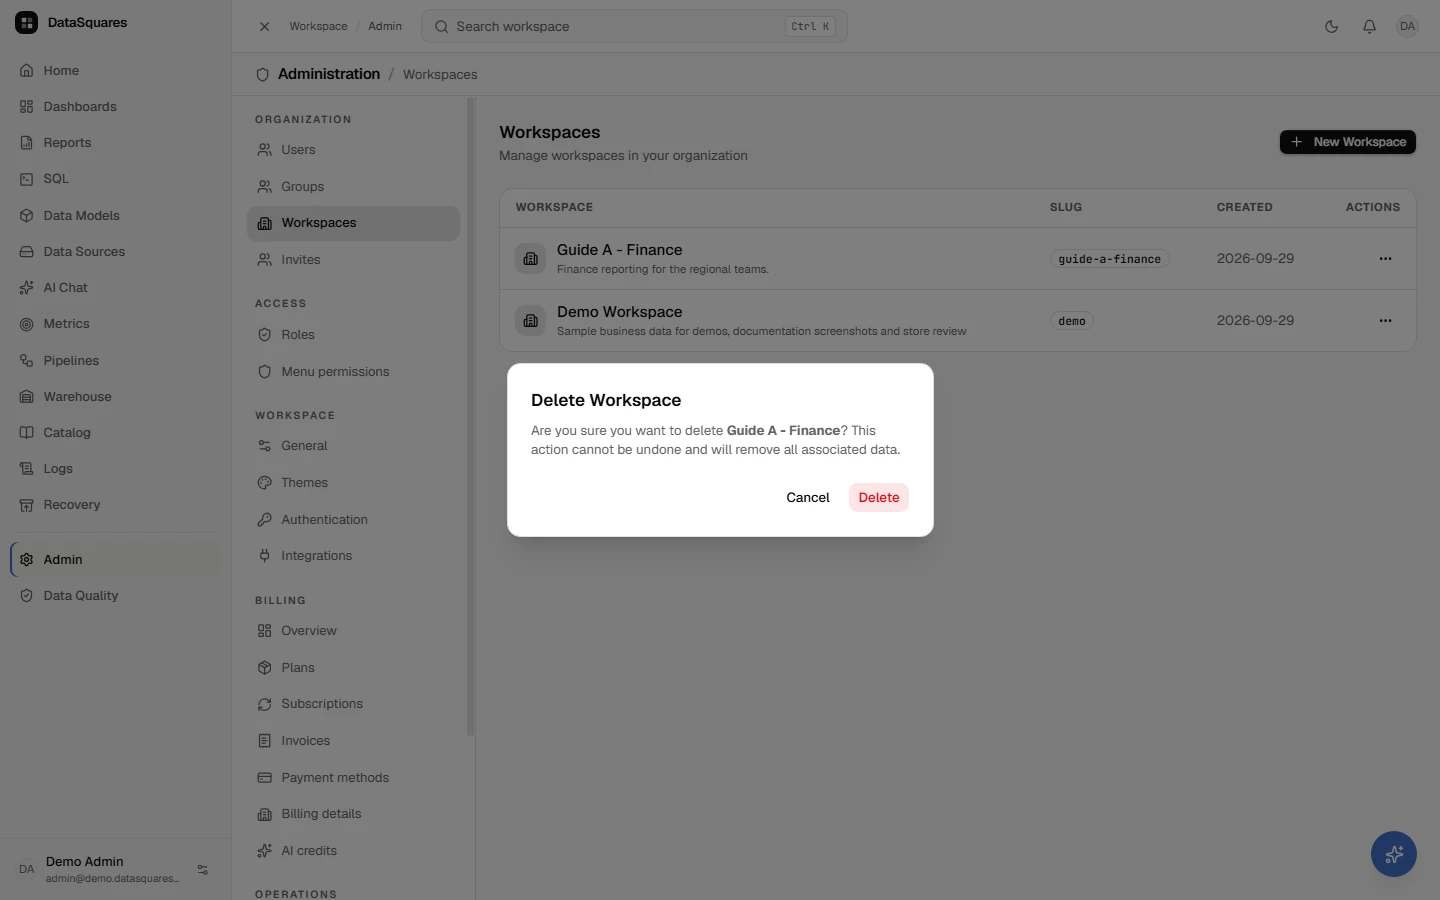
Choose Delete on the workspace to remove it together with what it holds. Do this only when nothing in it is still needed.
Invitations
Section titled “Invitations”The Invites tab (/admin/invites) manages team onboarding:
- Send Invitation: Specify the recipient’s email address, company role (
MemberorAdmin), and initial workspace role. There is no plan to choose: everyone joins on your company’s plan, which the form names beside the seats (one plan for your company). - Lifecycle Tracking: Monitor pending invitations, resend expired invite emails, or revoke pending invitations.
- Activation Flow: The invited user receives a secure tokenized link, confirms their email address, sets a password that follows the password rules, and enters the workspace.
Walkthrough: send an invitation
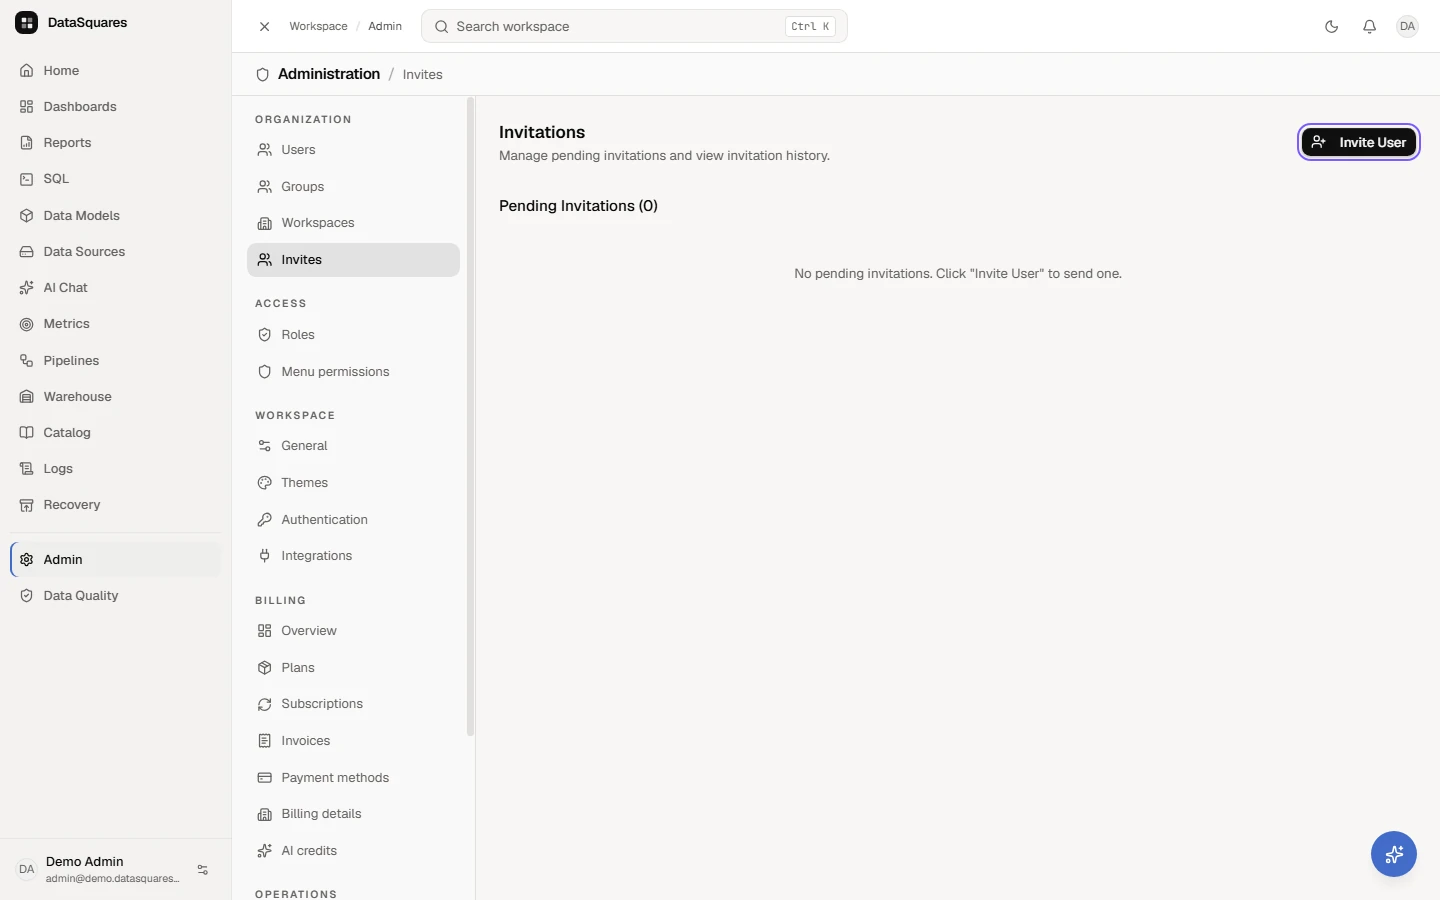
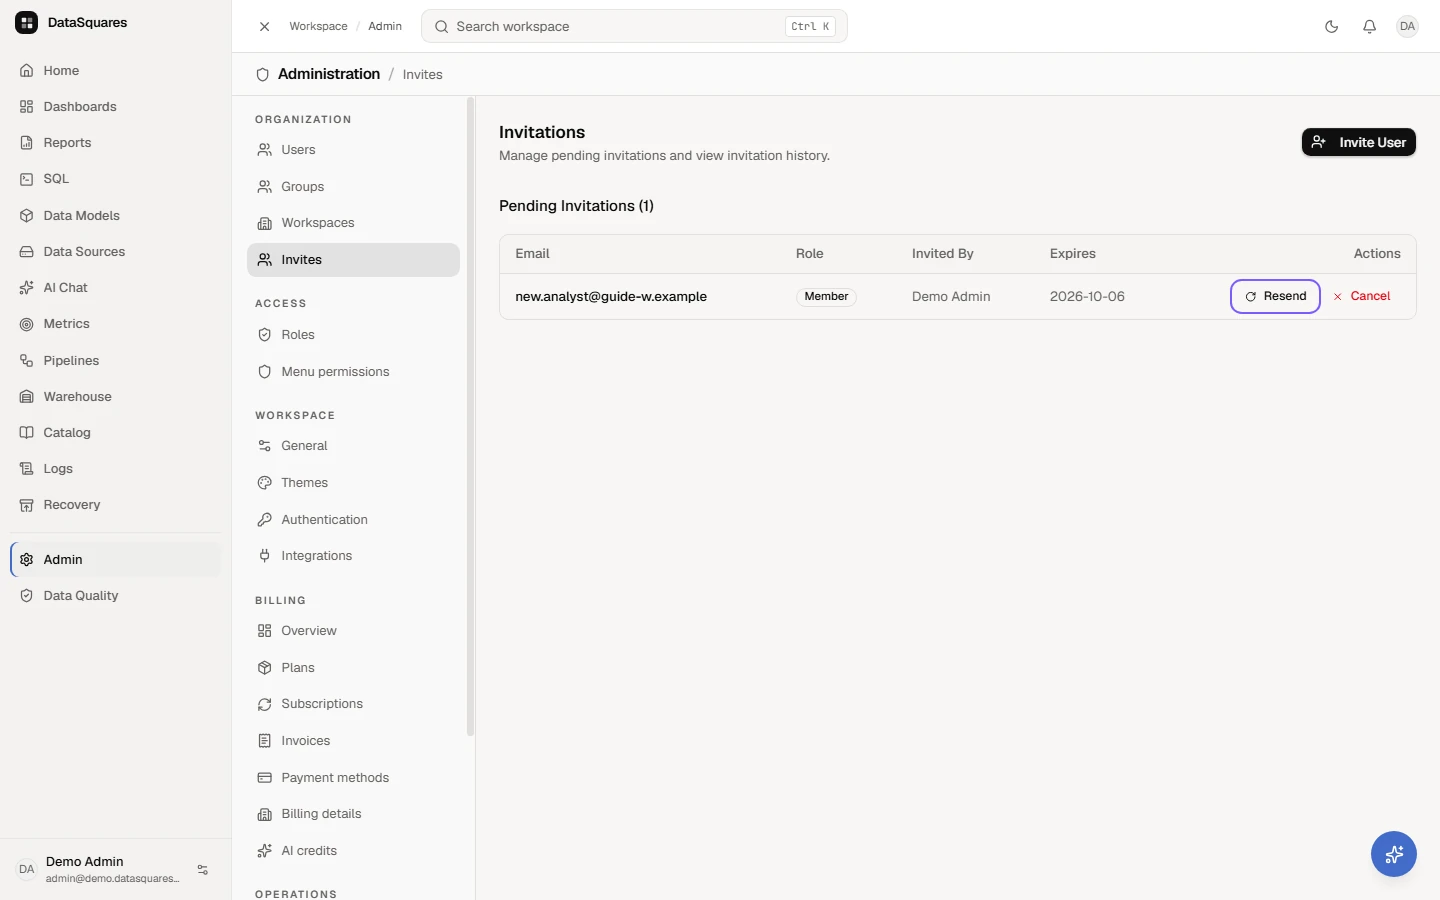
Section titled “Walkthrough: send an invitation”Open Admin, then Invites. Pending invitations wait here until they are accepted, cancelled or expire. Choose Invite User.
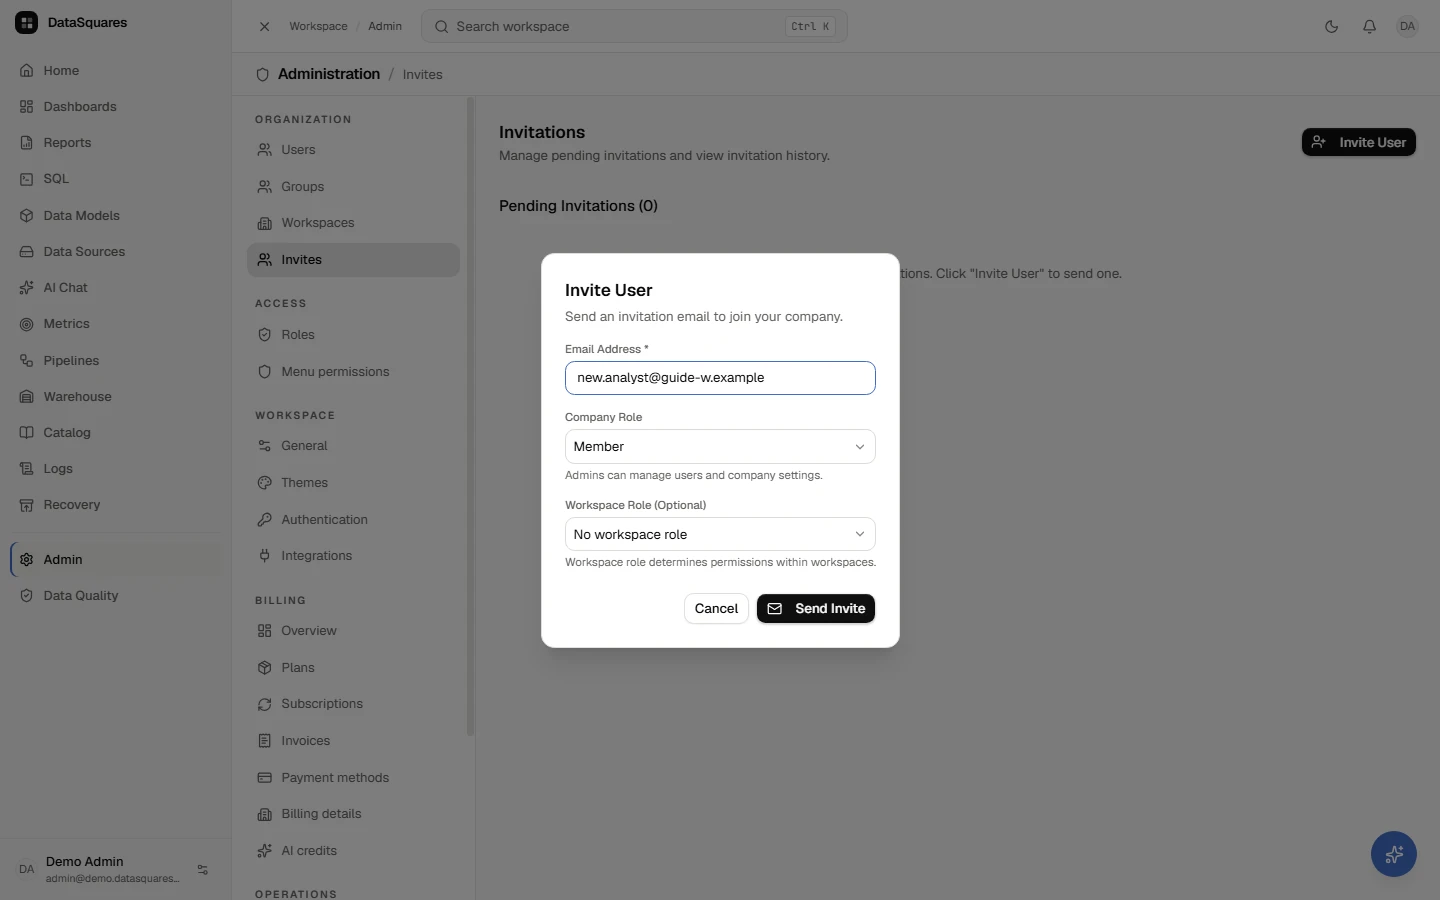
Enter the email address, choose a company role (Member or Admin) and, optionally, a workspace role for the person to start with. Where seats are limited the dialog also says whether one is free.
Choose Send Invite. DataSquares emails the invitation, and the person appears under Pending Invitations with who invited them and when the invitation Expires.
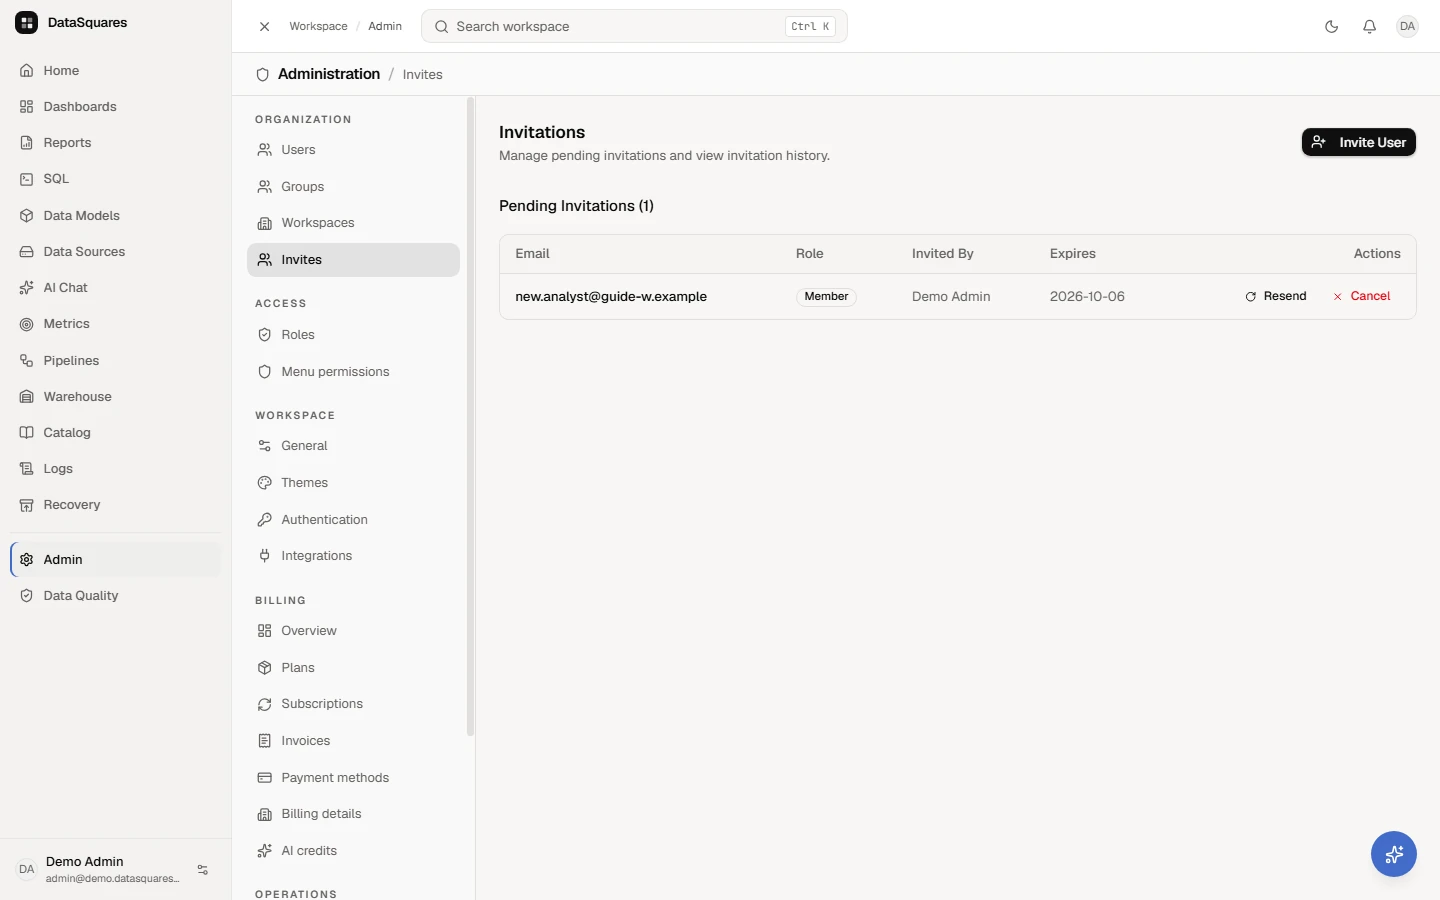
Resend sends a fresh link if the first one was lost; Cancel withdraws the invitation. Both act at once, without a confirmation.
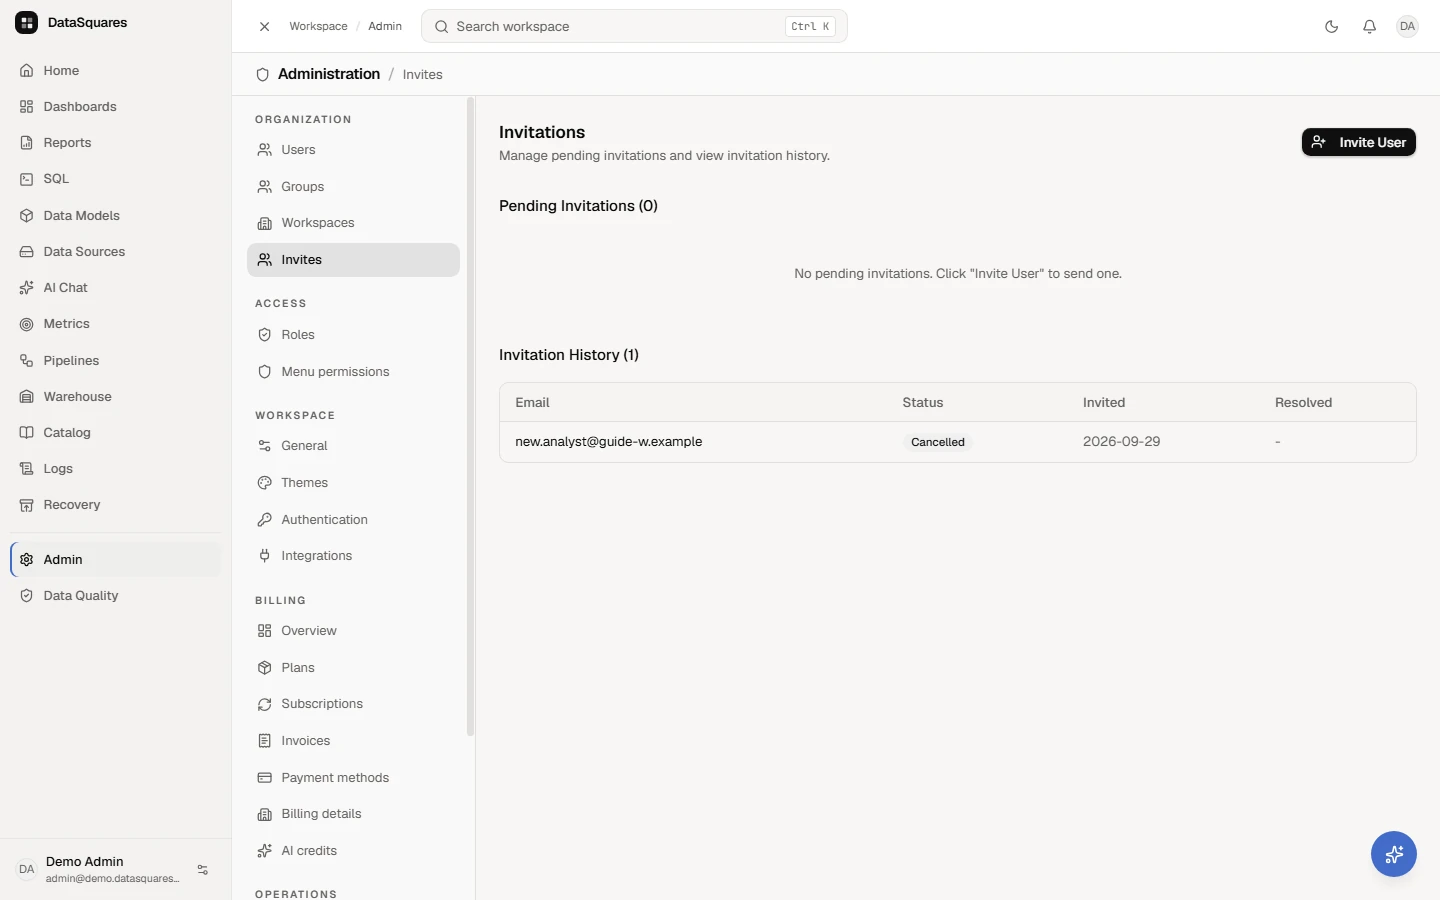
A cancelled invitation leaves Pending Invitations and moves to Invitation History, which lists every invitation that is no longer pending with its status (Accepted, Cancelled or Expired) and when it was invited and resolved. A cancelled link can no longer be used.
Walkthrough: accept an invitation
Section titled “Walkthrough: accept an invitation”The invited person opens the link from the invitation email. If no account exists yet for the address, which is the case for every invitation sent from Admin, then Invites, the page asks for Your name as well as a password.
Open the link from the invitation email. DataSquares checks it and shows the company you are joining and the email address the invitation is for. Because no account exists yet, the page also asks for Your name.
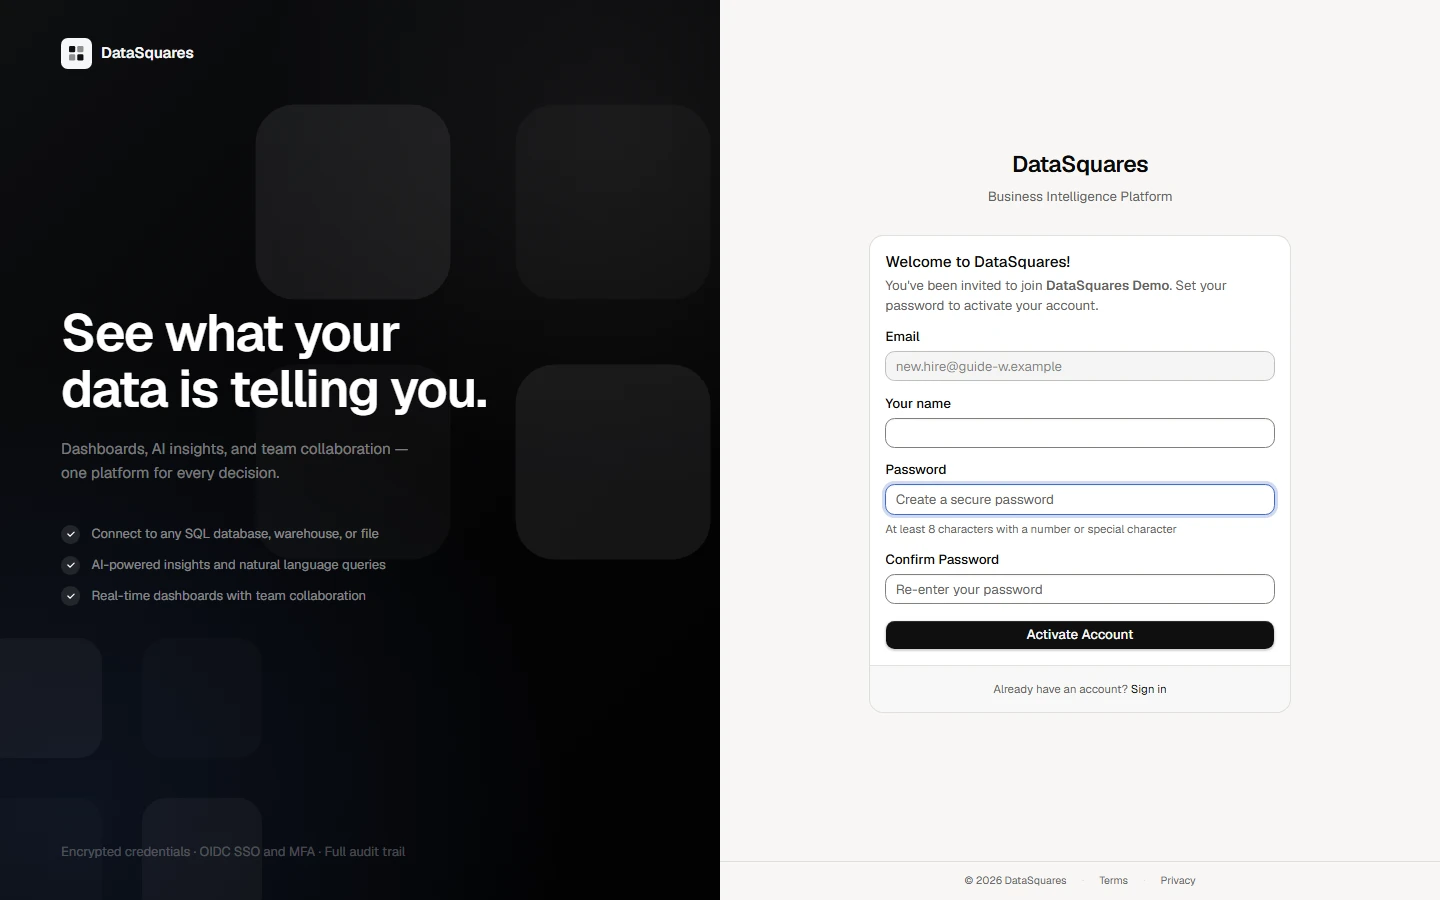
Type your name, choose a password and type it again to confirm it. Both password fields are masked.
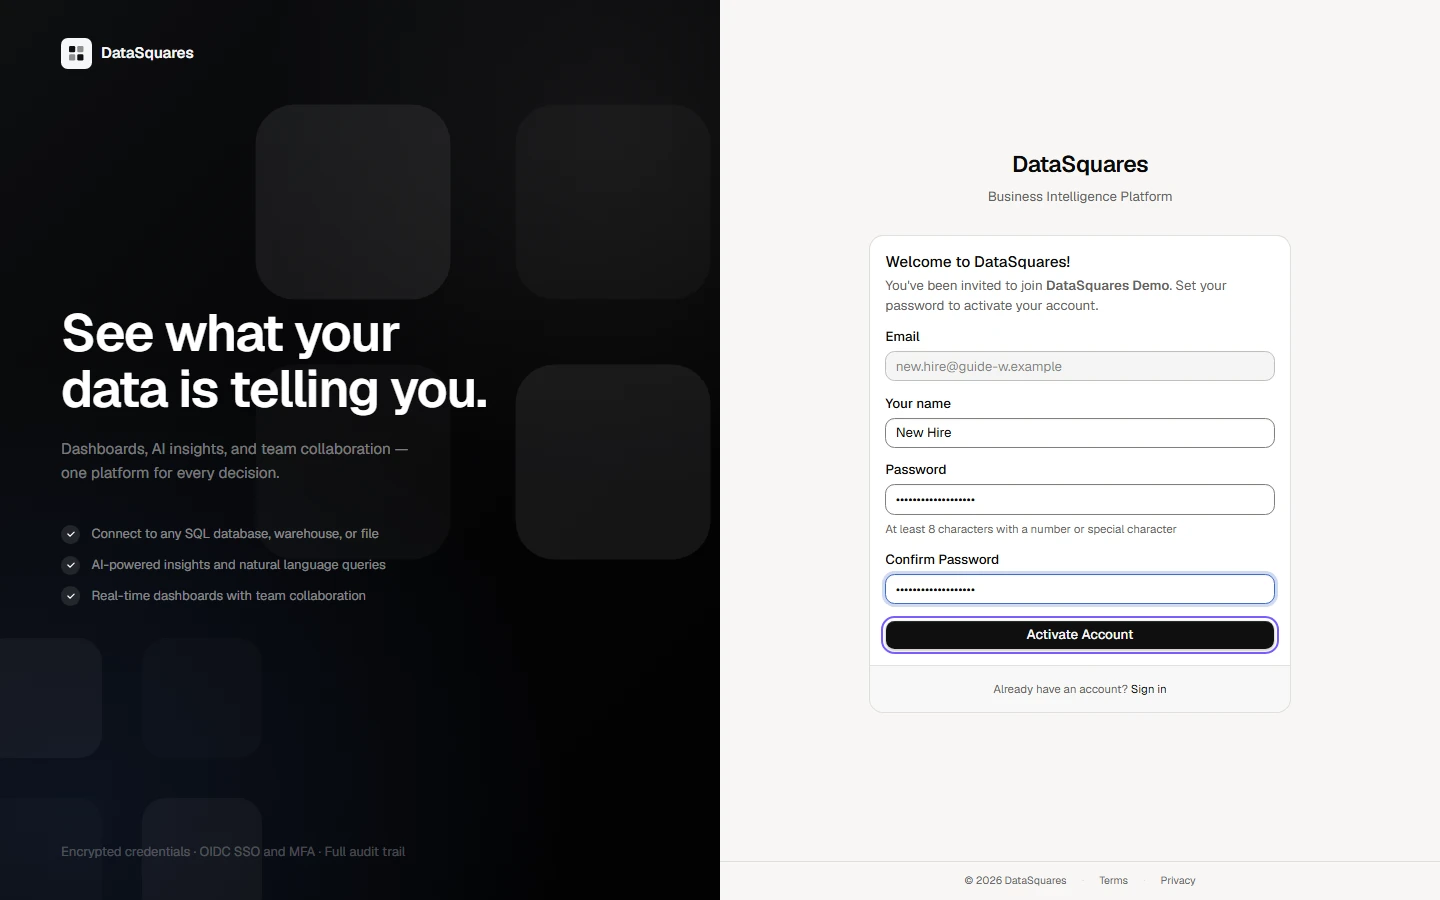
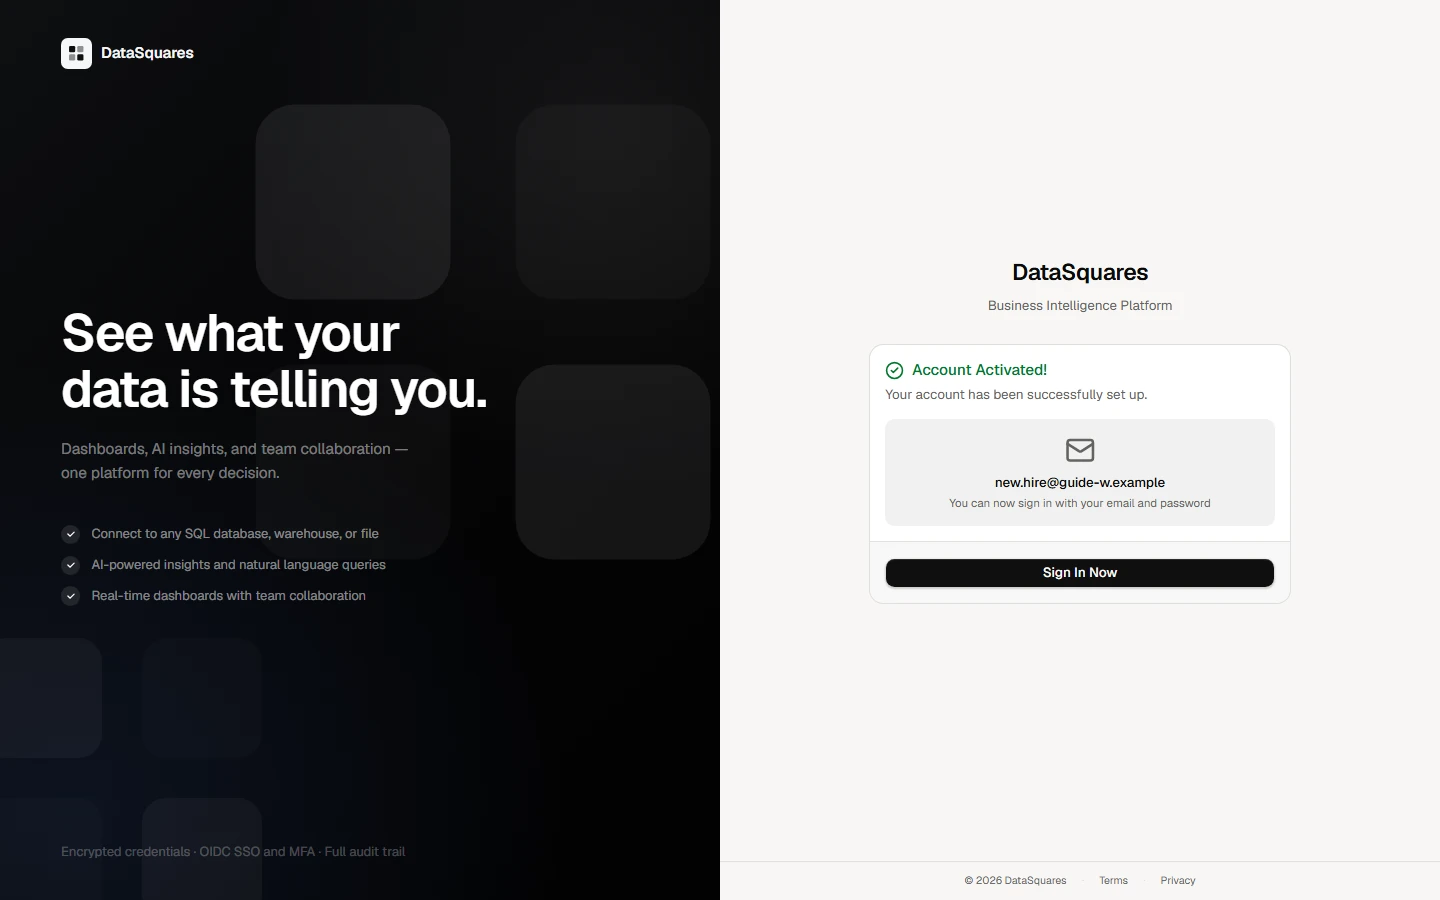
Choose Activate Account. The account is activated and the page says Account Activated! and offers Sign In Now; sign in with your email and the new password.
Related
Section titled “Related”- SSO & MFA — enterprise SAML, OIDC, and multi-factor authentication.
- Workspace settings & operations — workspace preferences, AI settings and limits, and API keys.
- Audit log — tracking user sign-ins, role modifications, and admin actions.